Learn how to integrate a SCIM with Strata Cloud Manager for automated user
provisioning, streamlined identity management, and enhanced security compliance across your
deployment.
Integrating a third-party System for Cross-Domain Identity Management (SCIM) enables you
to streamline identity and access management for Strata Cloud Manager. By connecting an
external identity provider such as SailPoint, Oracle Cloud Infrastructure (OCI), or
Okta, SCIM automates user provisioning, deprovisioning, and access control, establishing
a centralized and consistent approach to identity lifecycle management. This integration
reduces manual administrative effort, helps enforce uniform access policies, and ensures
that user and access information remains accurate and up to date across connected
systems.
To set up an integration with a third-party SCIM, you configure a Tenant Service Group
(TSG) and service account in your system, followed by setting up the SCIM connector in
the third-party provider. For those seeking maximum control and security, optional
features like SCIM-only mode ensure that all Access Management changes occur exclusively
through the SCIM connector.
Supported SCIM Providers
Strata Cloud Manager supports integration with the following SCIM providers:
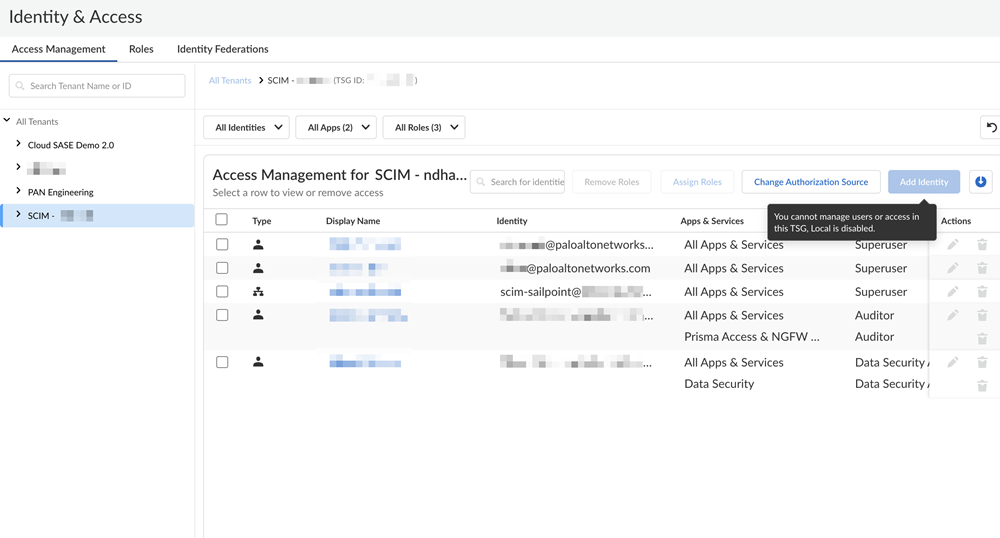
After the SCIM integration is enabled for Strata Cloud Manager, all
access management changes will only be allowed through the SCIM
provider.
Set up the SCIM to manage access for Strata Cloud Manager.
For the most up-to-date instructions on managing a SCIM Connector, see the
SailPoint documentation.
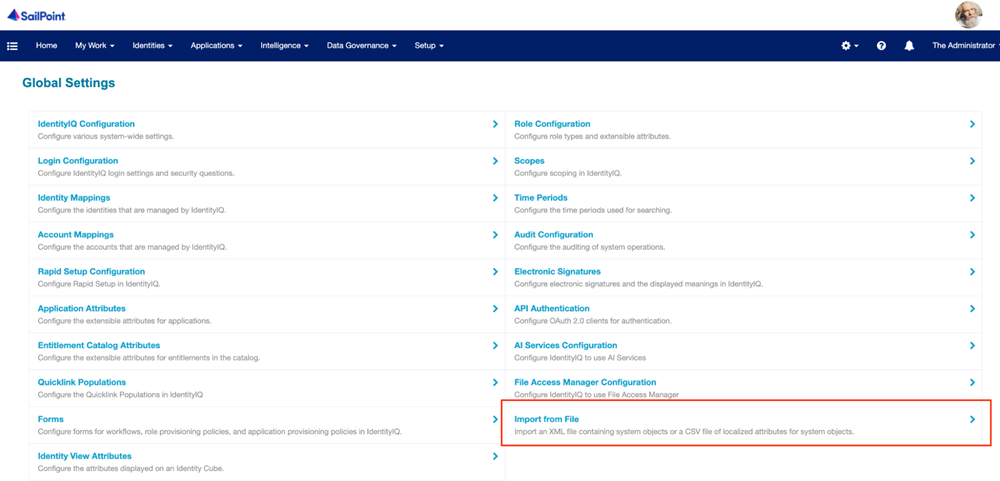
Import the XML file containing the Strata Cloud Manager SCIM Connector
configuration into Sailpoint (this XML file will be provided by your
account representative).
After importing the XML, the application will display under the
Application Definition.
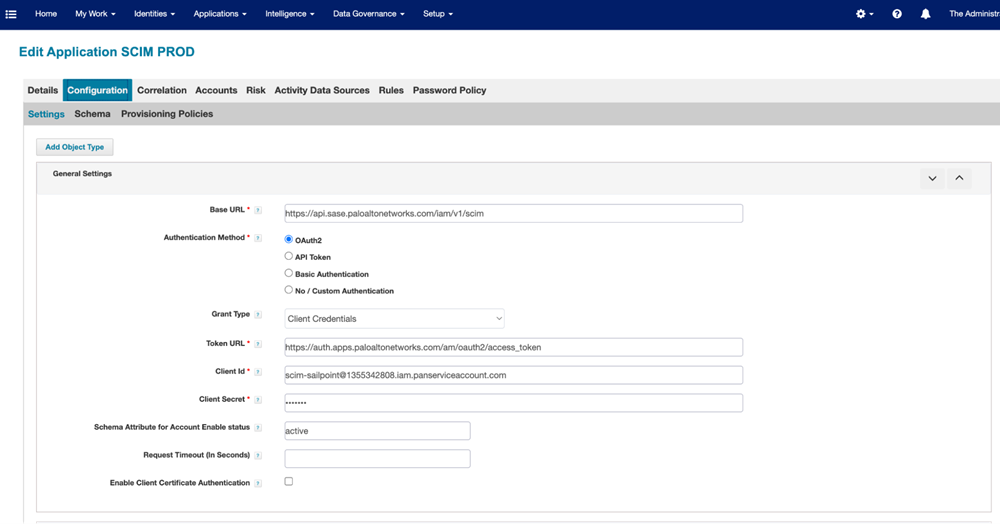
Select the application and enter the OAuth2 client credentials from the
service account you created in Strata Cloud Manager.
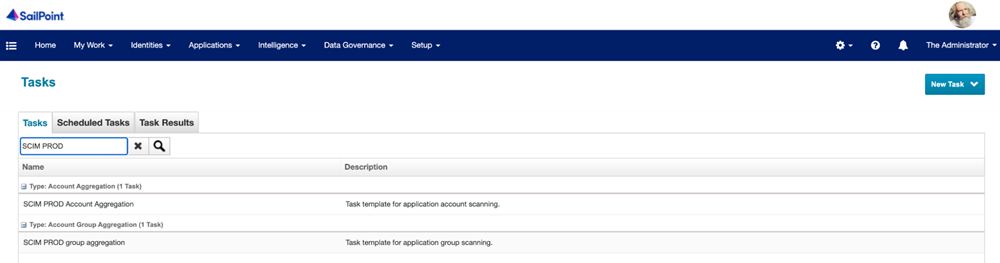
Set up Aggregation Tasks in SailPoint for Accounts and Groups for the
SCIM Connector.
This ensures that all relevant identity data from Strata Cloud Manager is efficiently integrated into SailPoint, enabling better
identity governance, streamlined access management, and enhanced
security.
OCI
Enhance identity management in SCM with an advanced SCIM integration for OCI,
automating user and group provisioning.
This procedure outlines the steps to configure SCIM-based user and group provisioning
between OCI and Strata Cloud Manager. By automating identity and access management,
you can enhance security and improve operational efficiency within your Strata Cloud Manager environment. Follow these steps to set up the integration:
Set up Strata Cloud Manager to use SCIM-based provisioning for identity access
management.
After SCIM integration is enabled for Strata Cloud Manager, all
access management changes are permitted only through the configured
third-party IdP using the SCIM protocol.
Configure OCI to provision users and groups to Strata Cloud Manager using the
integrated application in OCI to connect with Strata Cloud Manager.
For the most up-to-date instructions on configuring SCIM provisioning in OCI,
refer to the OCI documentation.
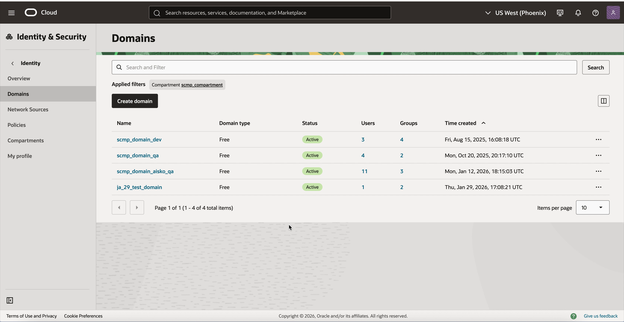
Log in to Oracle Cloud Infrastructure (OCI).
Select Identity & SecurityDomains and then select your domain where your users and groups
reside.
Search and select the appropriate application template, for example, a
custom SCIM application or a generic enterprise application.
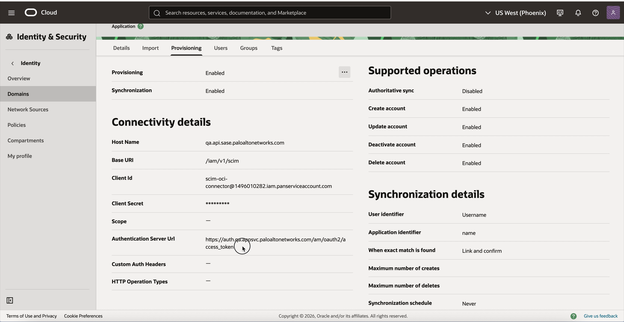
Configure the provisioning settings for the application.
Select the provisioning method as Client
Credentials.
Specify:
Host Name - Your Strata Cloud Manager API
endpoint.
Base URL - Specify /iam/v1/scim.
Client ID - The service account ID obtained from
Strata Cloud Manager (see STEP 1.ii).
Client Secret - The bearer token generated for
the service account in Strata Cloud Manager (see STEP
1.ii).
Authentication Server URL - Your Strata Cloud Manager authentication endpoint
(https://auth.paloaltonetworks.com/am/oauth2/access_token).
Test Connectivity to verify that OCI can successfully establish
a connection and authenticate with the Strata Cloud Manager SCIM
endpoint.
Select Refresh Application Data to retrieve
available Strata Cloud Manager access policies (roles or groups) from
Strata Cloud Manager.
Select ImportRun Import to import existing users and groups from Strata Cloud Manager into OCI.
Assign Users and Access Policies in OCI for Strata Cloud Manager
Synchronization.
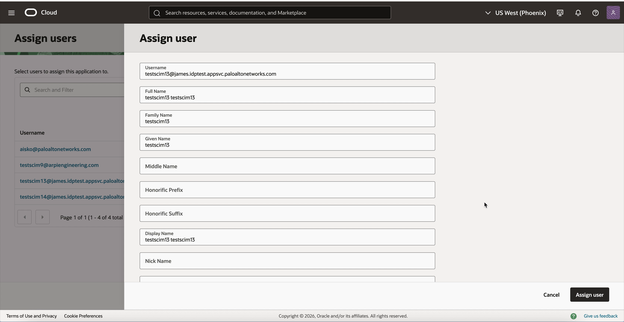
Select UsersAssign Users and then select the user or users you wish to
provision to Strata Cloud Manager.
Figure 6: Selecting a user to assign to the SCIM application
in OCI.
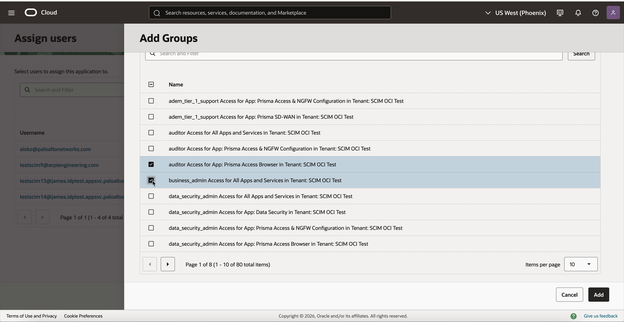
In the assignment details, select
Groups and select the Strata Cloud Manager access policies you want to apply to
these users.
Assign Users to apply the associated Strata Cloud Manager access policies to the user.
Note: Ensure that these users email domains are
verified by the Strata Cloud ManagerIdentity
Federation.
Verify user provisioning in Strata Cloud Manager.
Log in to Strata Cloud Manager.
Navigate to Identity & Access ManagementUsers.
Search for the user provisioned in the previous step.
Verify that the user account exists and has the correct group
assignments.
Okta
Configure Okta as a SCIM provider to automate user provisioning and group
synchronization with Strata Cloud Manager.
SCIM-based integration with Okta enables automated user provisioning, group
synchronization, and streamlined identity lifecycle management for Strata Cloud Manager. This integration uses OAuth 2.0 Client Credentials for
authentication between Okta and the Strata Cloud Manager SCIM endpoint, with a
dedicated service account providing the required API access.
Enable SCIM authorization source in Strata Cloud Manager.
This step configures Strata Cloud Manager to accept identity and access
management changes through a SCIM provider. After enabling SCIM, all user
provisioning and role assignments must be performed through the connected
SCIM provider.
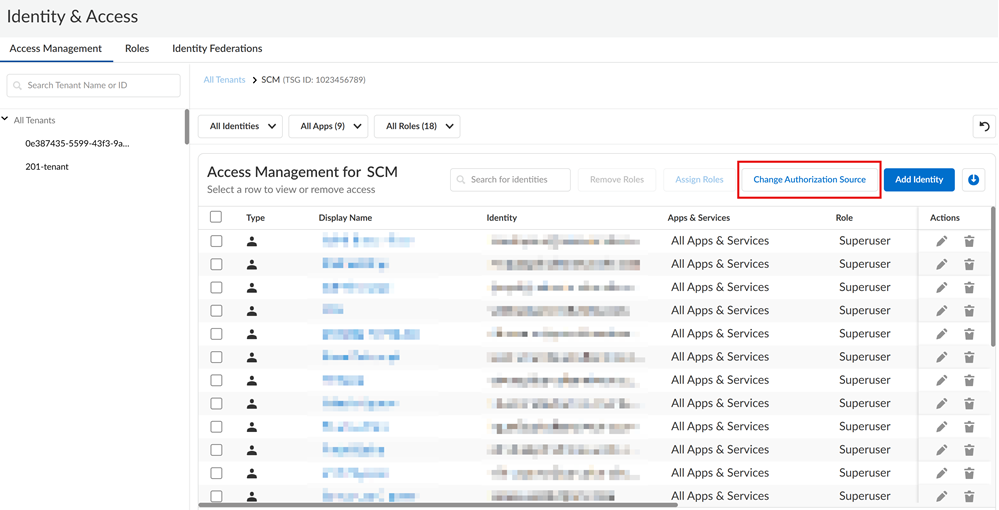
Use one of the various ways to access Common Services > Identity
& Access.
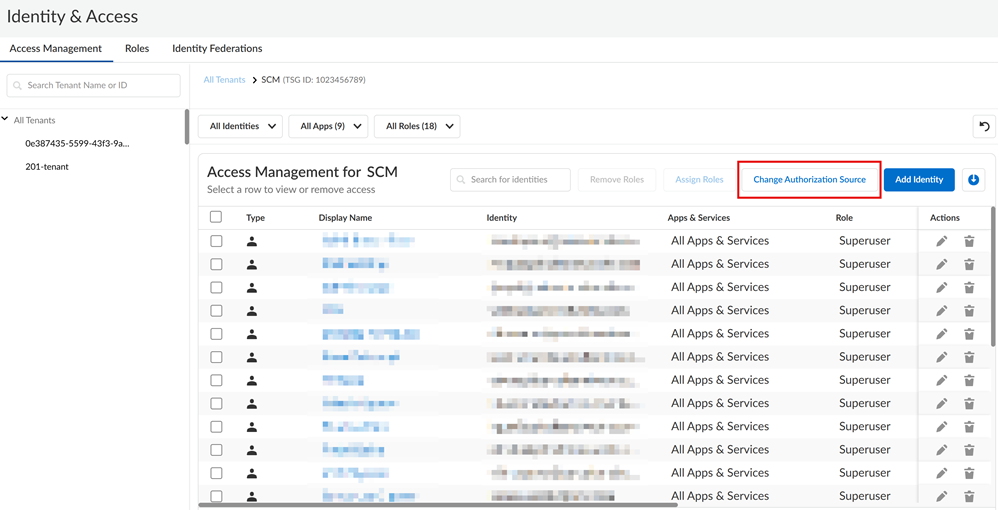
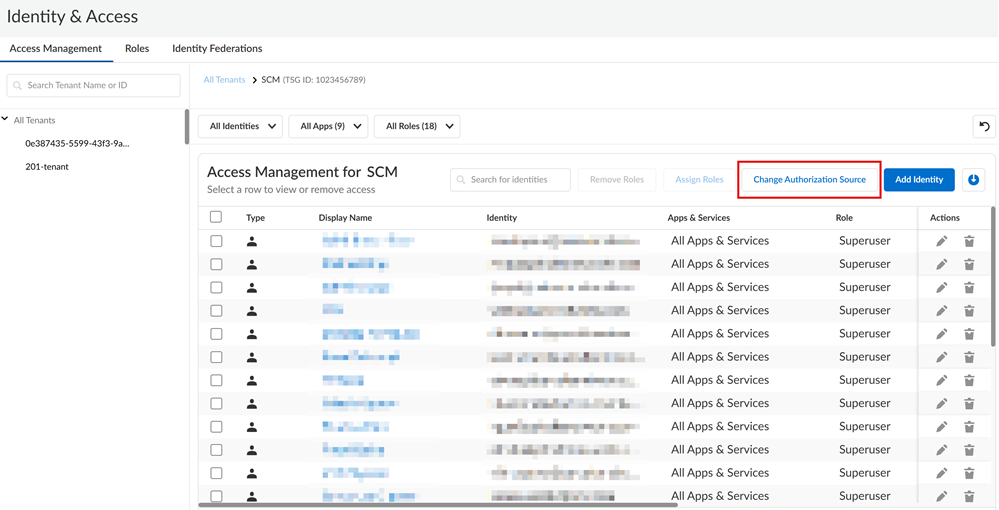
Select Identity & AccessAccess Management.
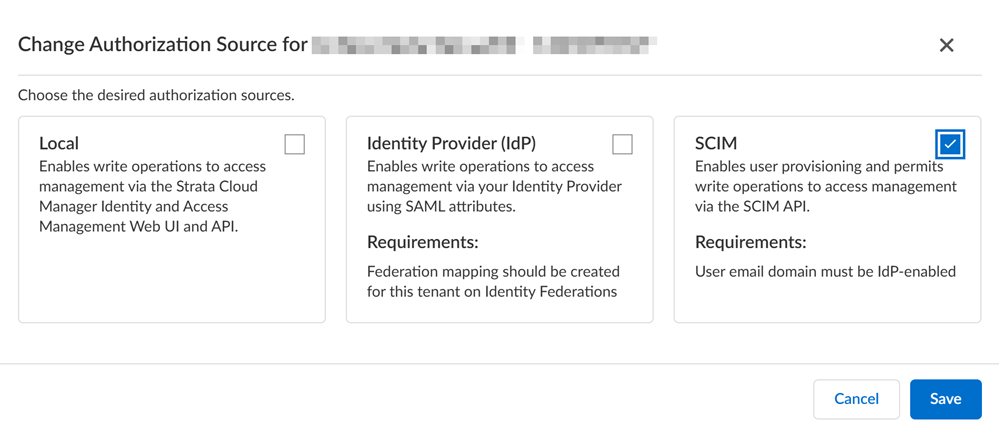
Click Change Authorization Source.
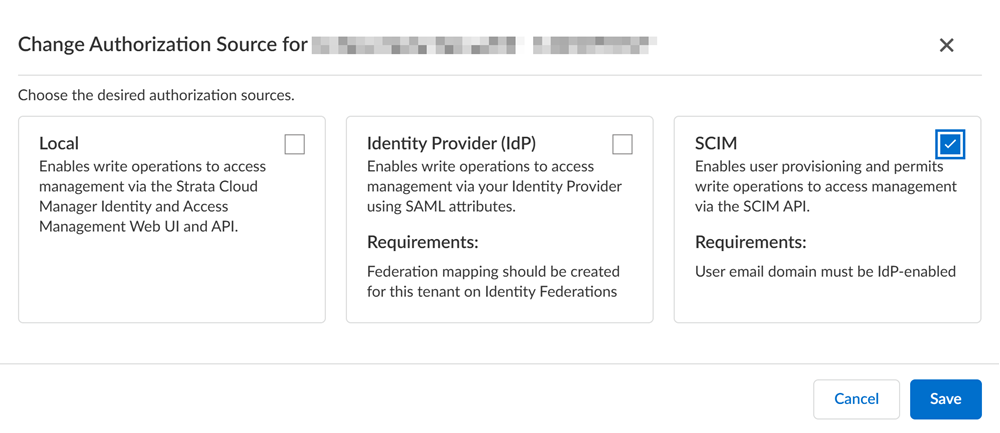
Enable SCIM and then click
Save to apply your changes.
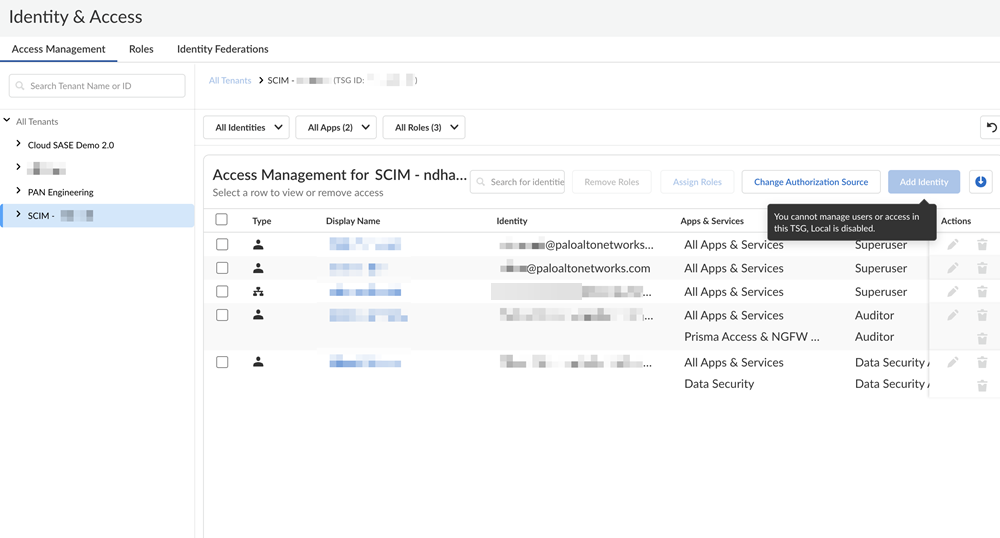
After SCIM integration is enabled, all access management changes are
permitted only through the configured third-party identity provider
using the SCIM protocol.
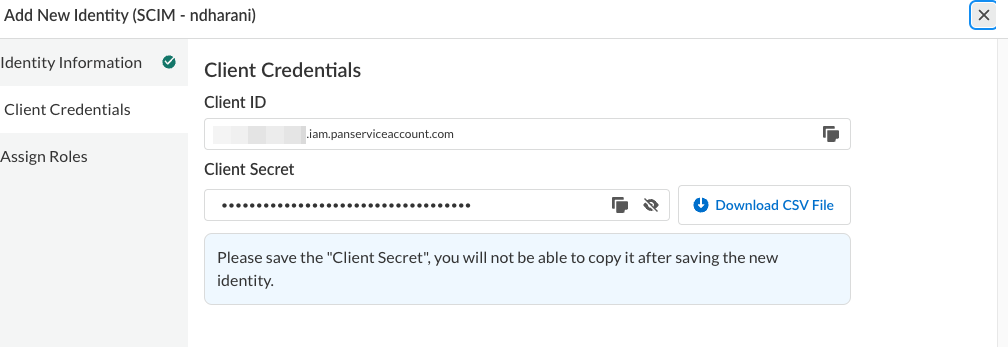
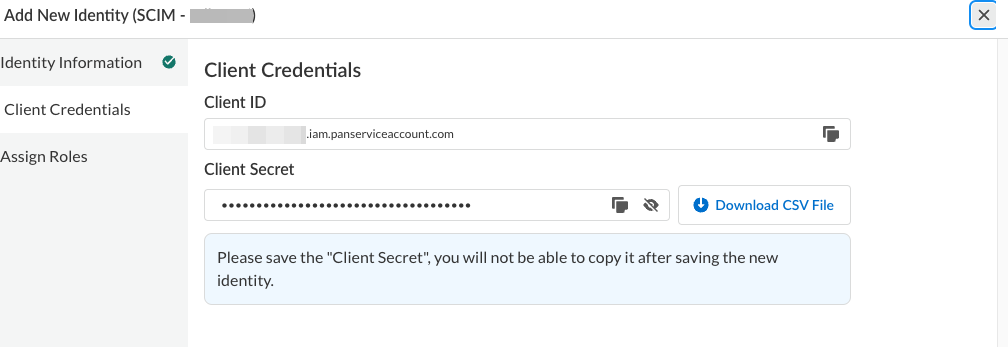
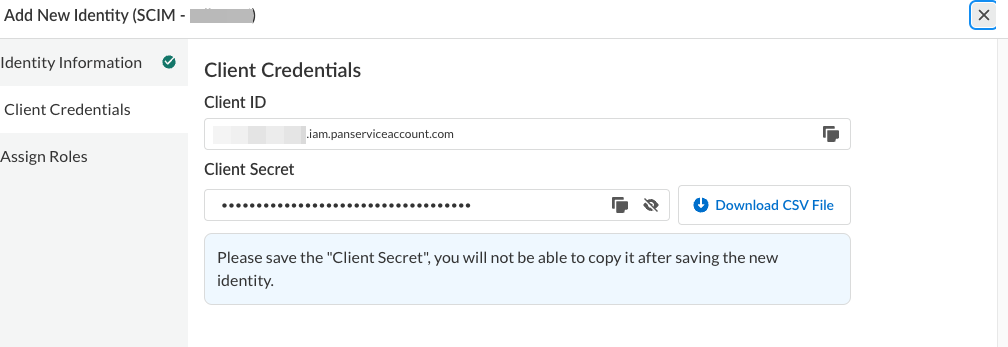
Create a service account in Strata Cloud Manager.
Create a service account that provides the OAuth 2.0 credentials Okta uses to
authenticate with the Strata Cloud Manager SCIM endpoint. The service
account must have the IAM Administrator role to perform SCIM
operations.
You need these credentials when configuring the SCIM connection in
Okta.
The Client Secret is shown only once during creation. Store it
securely. The service account is used solely for API authentication —
users cannot log in to Strata Cloud Manager with these
credentials.
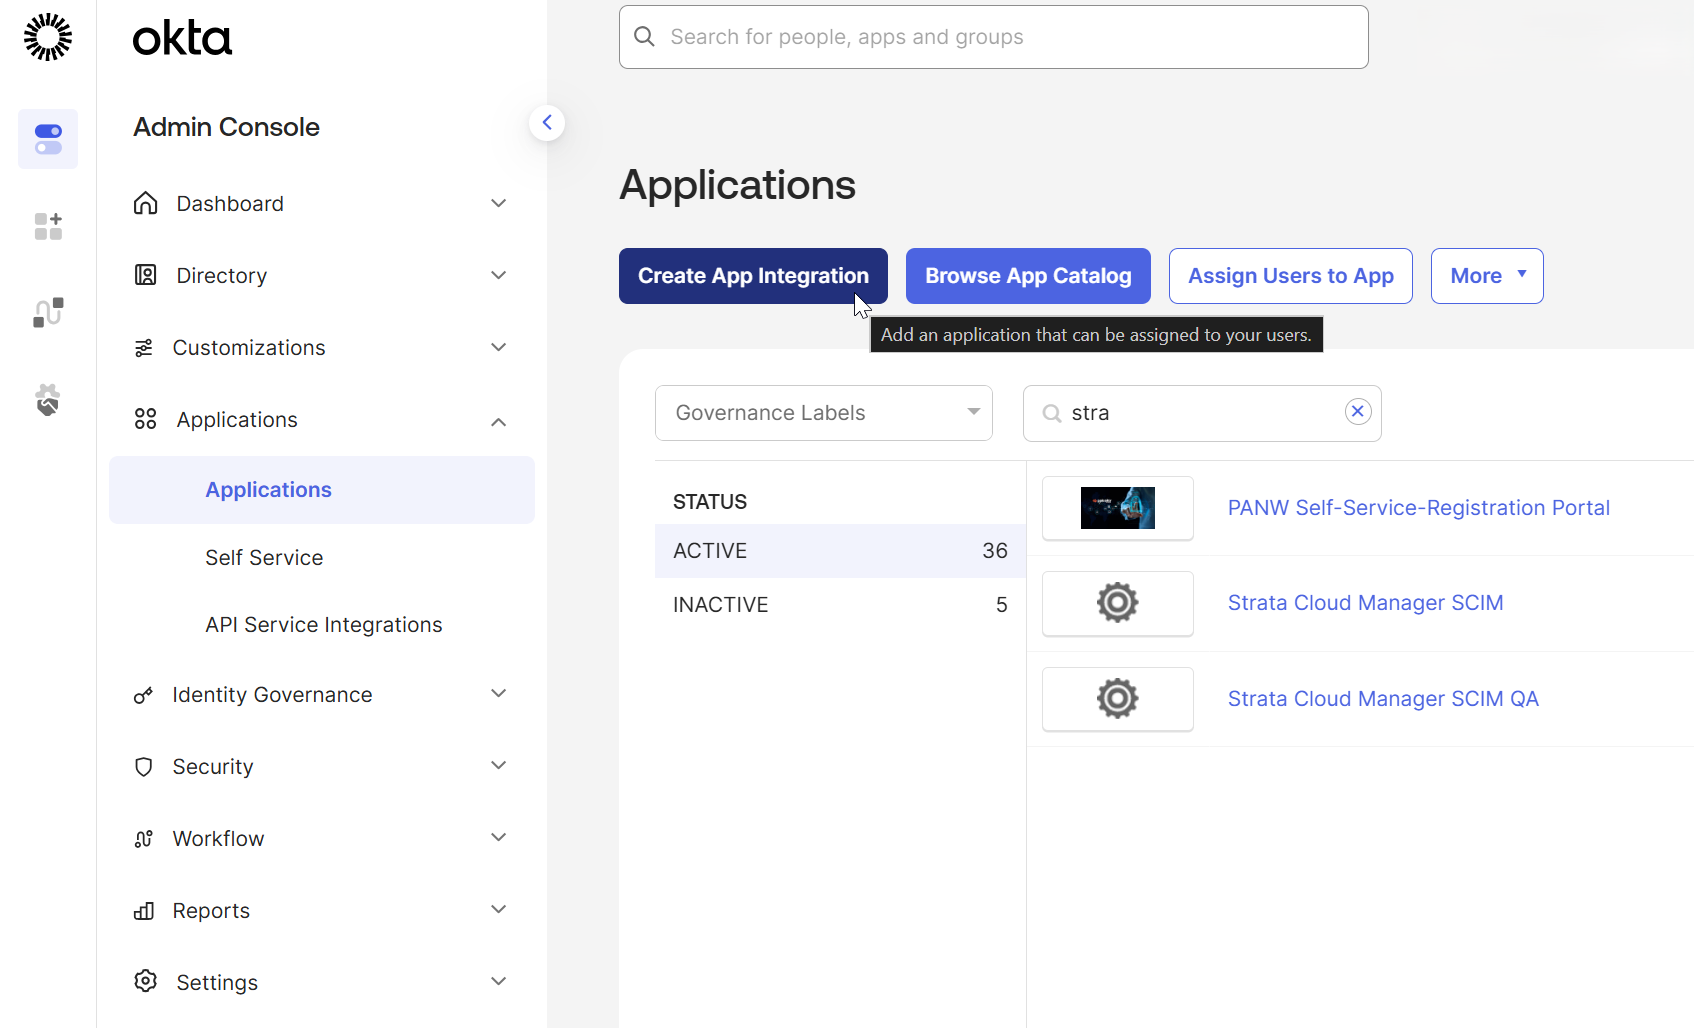
Create and configure an Okta application.
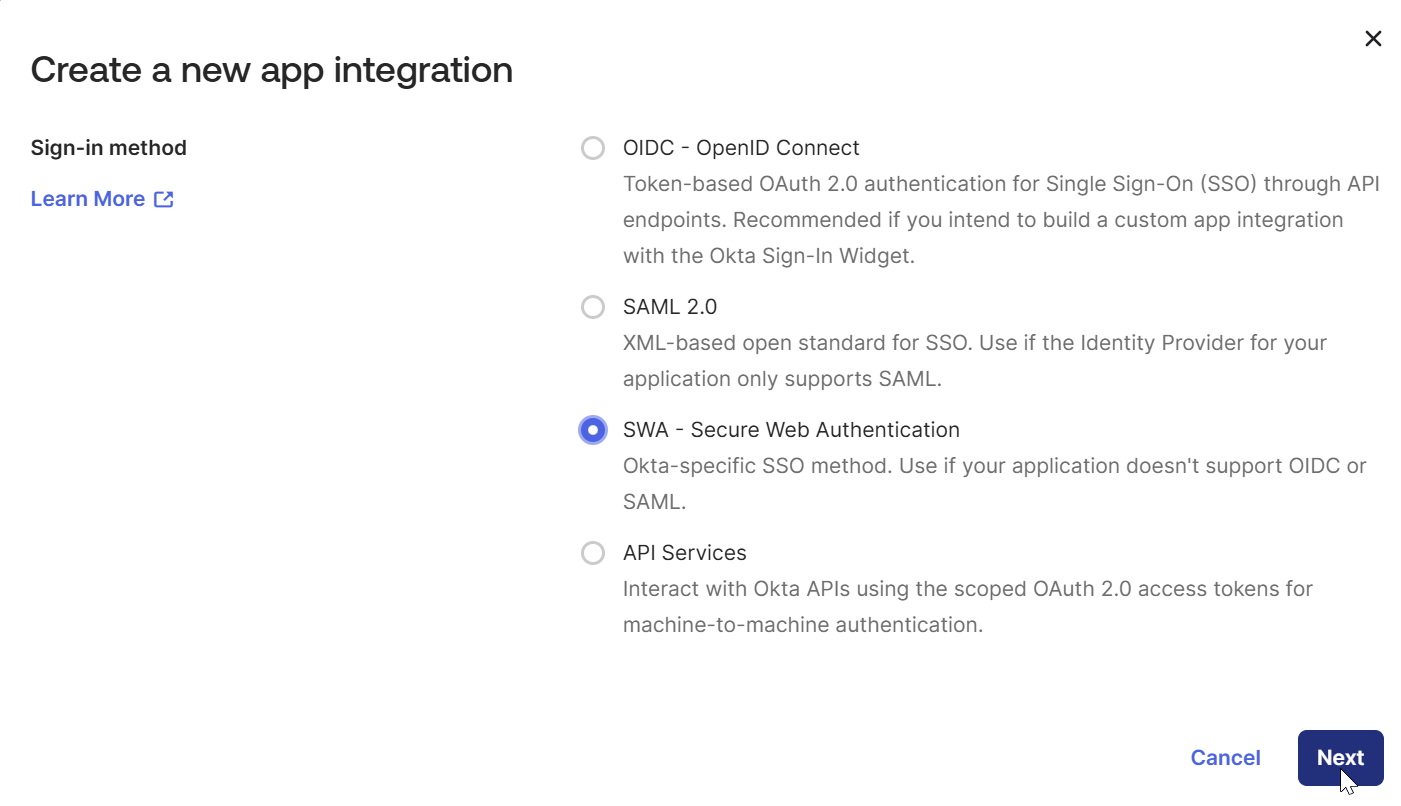
Create a Secure Web Authentication (SWA) application in Okta and enable SCIM
provisioning for it. This application serves as the integration point
between Okta and the Strata Cloud Manager SCIM endpoint.
Choose SWA - Secure Web Authentication as the
sign-in method and click Next.
Configure the application settings:
App Name — Specify an application name (for example,
SCM SCIM Integration).
App's login page URL — Specify any URL in the
application URL field.
The application URL is not used for SCIM provisioning. SCIM is an
API-based integration, not a UI integration. You can enter any valid
URL string.
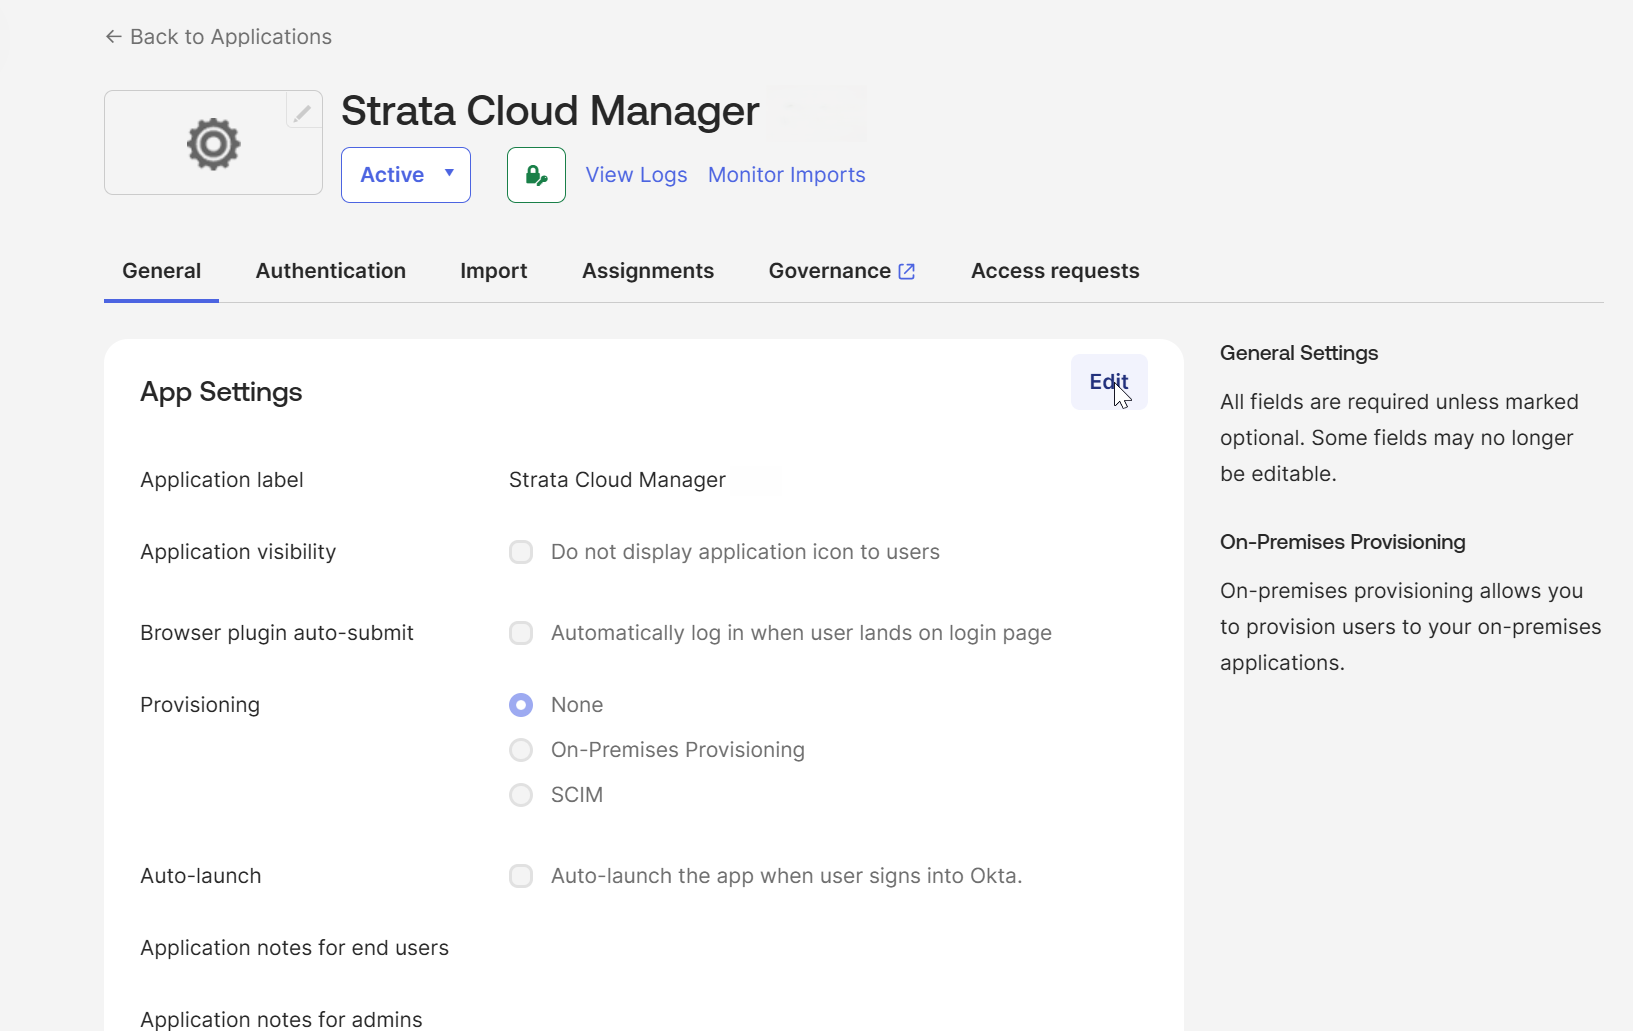
Enable SCIM provisioning.
In the application General tab, click
Edit in the app settings. Enable
SCIM provisioning, and click
Save.
After saving, a Provisioning tab appears in
the application settings.
Configure the SCIM connection in Okta.
Configure the SCIM connector settings and authenticate using the OAuth 2.0
credentials from the Strata Cloud Manager service account.
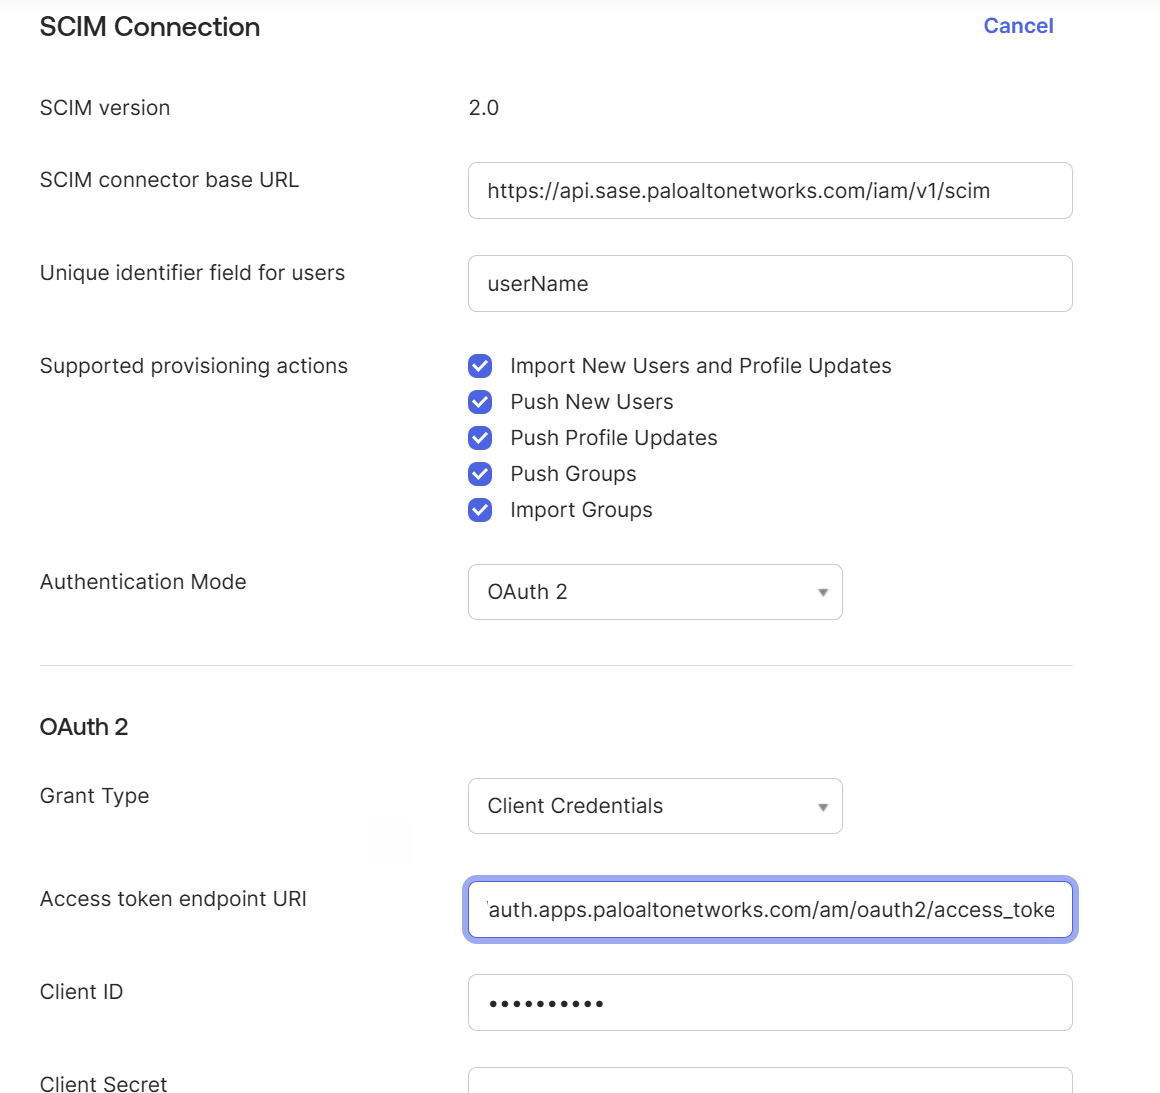
In the application, select ProvisioningEdit.
Configure the SCIM connection settings:
SCIM connector base URL — Enter the base URL of the SCIM
endpoint that Okta uses to provision users and groups to your
application. Set the value to
https://api.sase.paloaltonetworks.com/iam/v1/scim.
Unique identifier field for users — Specify the SCIM user
attribute that uniquely identifies each user. Set this value to
userName.
Supported provisioning actions — Select Import New Users,
Push New Users, Push Profile Updates, Push Groups, and Import
Groups.
Authentication Mode — Select OAuth 2 (Client
Credentials) to authenticate Okta with the SCIM
server using the OAuth 2.0 Client Credentials grant.
Configure the OAuth 2.0 authentication settings:
Access token endpoint — Specify the OAuth 2.0 token
endpoint that Okta uses to obtain an access token. Set this value
to
https://auth.apps.paloaltonetworks.com/am/oauth2/access_token.
Client ID — Specify the Client ID generated for the
service account that you created in Step 2.
Client Secret — Specify the Client Secret generated for
the service account that you created in Step 2.
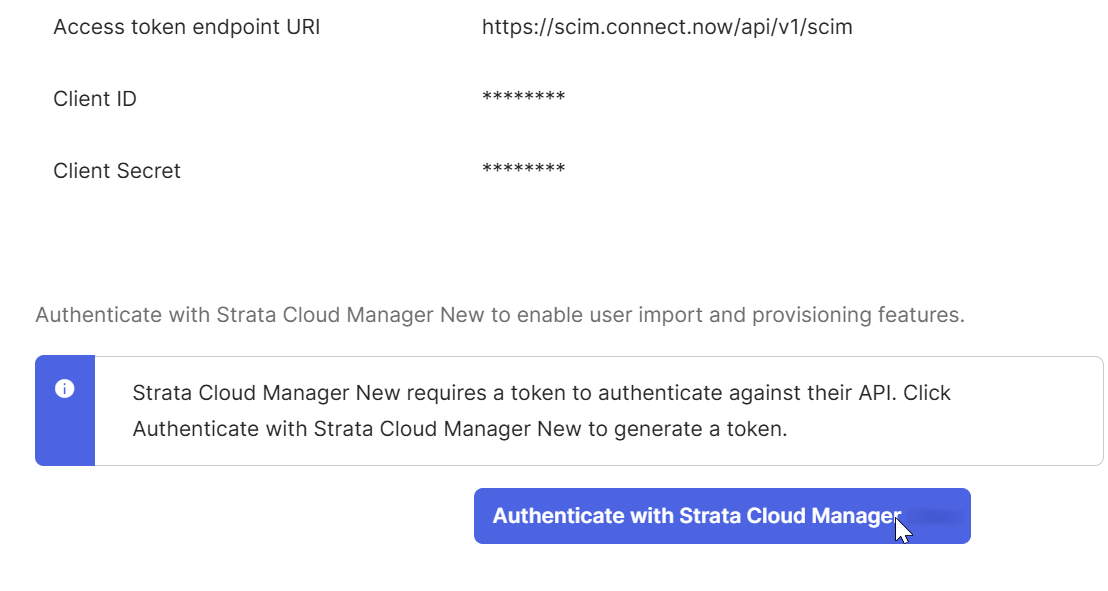
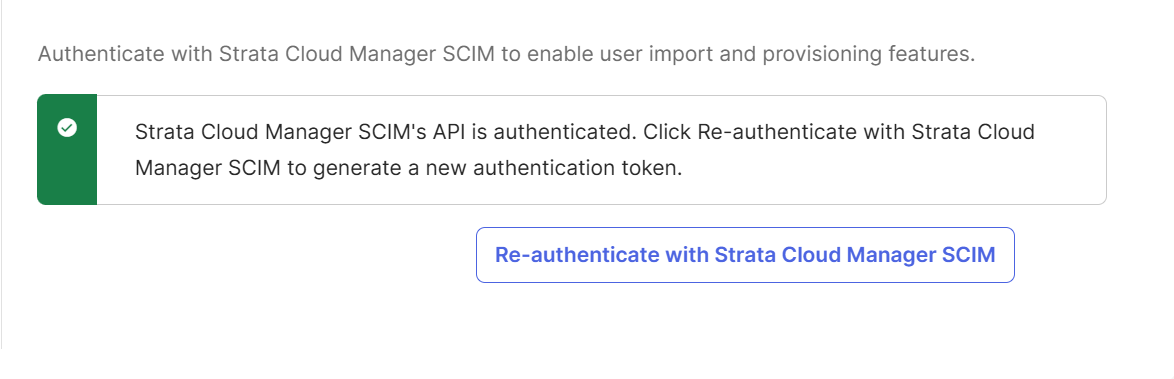
Authenticate with Strata Cloud Manager to verify that Okta can
authenticate and connect to the SCIM endpoint.
A success message confirms that the OAuth 2.0 authentication and SCIM
endpoint connectivity are working correctly.
Under ProvisioningTo App, click Edit and enable
Create Users, then click
Save.
You must enable Create Users to avoid
provisioning errors when pushing groups that contain users not yet
provisioned in Strata Cloud Manager.
Provision groups from Okta to Strata Cloud Manager.
Import existing Strata Cloud Manager roles into Okta, create an Okta user
group, and push the group to Strata Cloud Manager by linking it to a
predefined Strata Cloud Manager role.
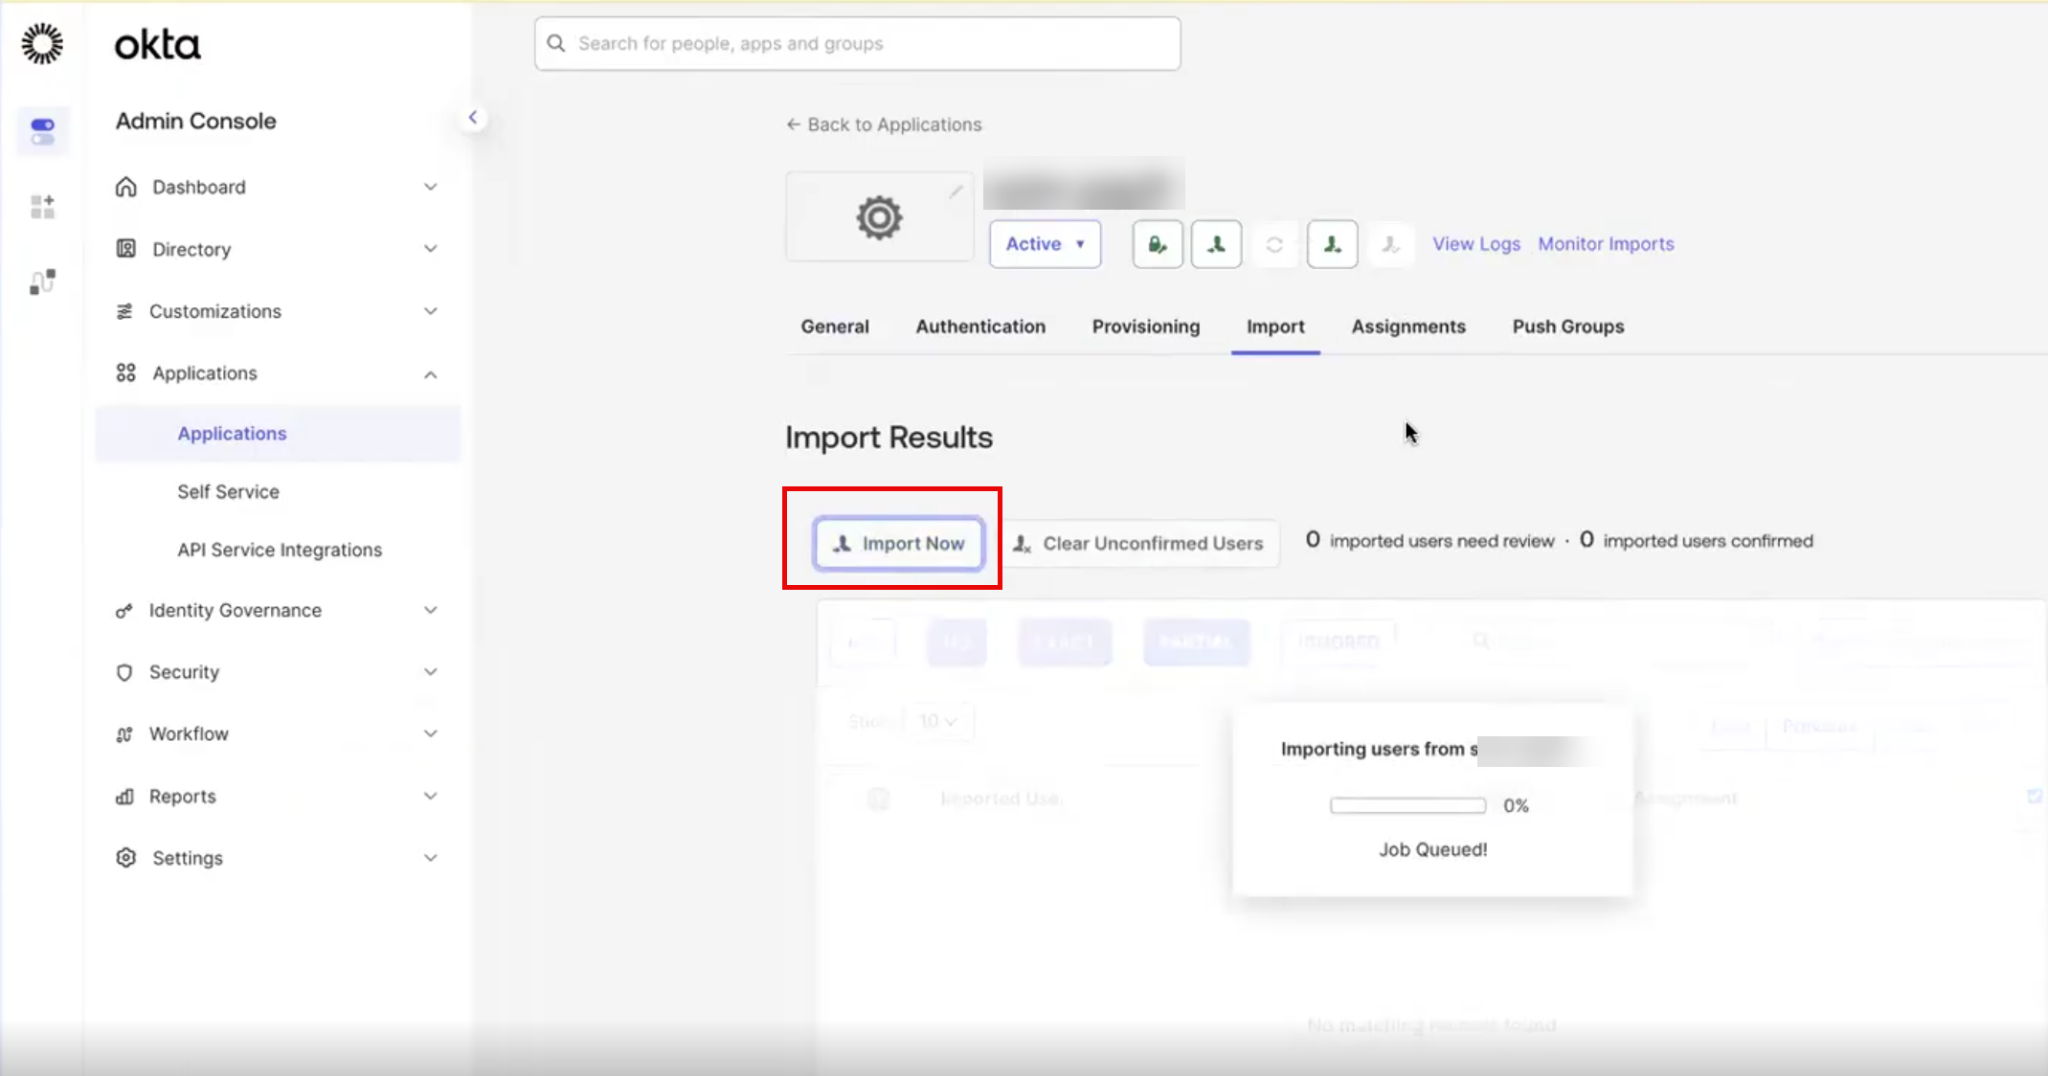
In the application, select ImportImport Now to retrieve the predefined access policies (roles) from
Strata Cloud Manager into Okta.
You must import groups from Strata Cloud Manager before assigning
or pushing any groups. Importing retrieves the predefined Strata Cloud Manager roles so they are available for linking in the
Push Groups step.
Create an Okta group.
Navigate to DirectoryGroups and click Add Group. Enter a
group name and click Save. Select the newly
added group and add the users you want to provision to this
group.
Assign the group to the application.
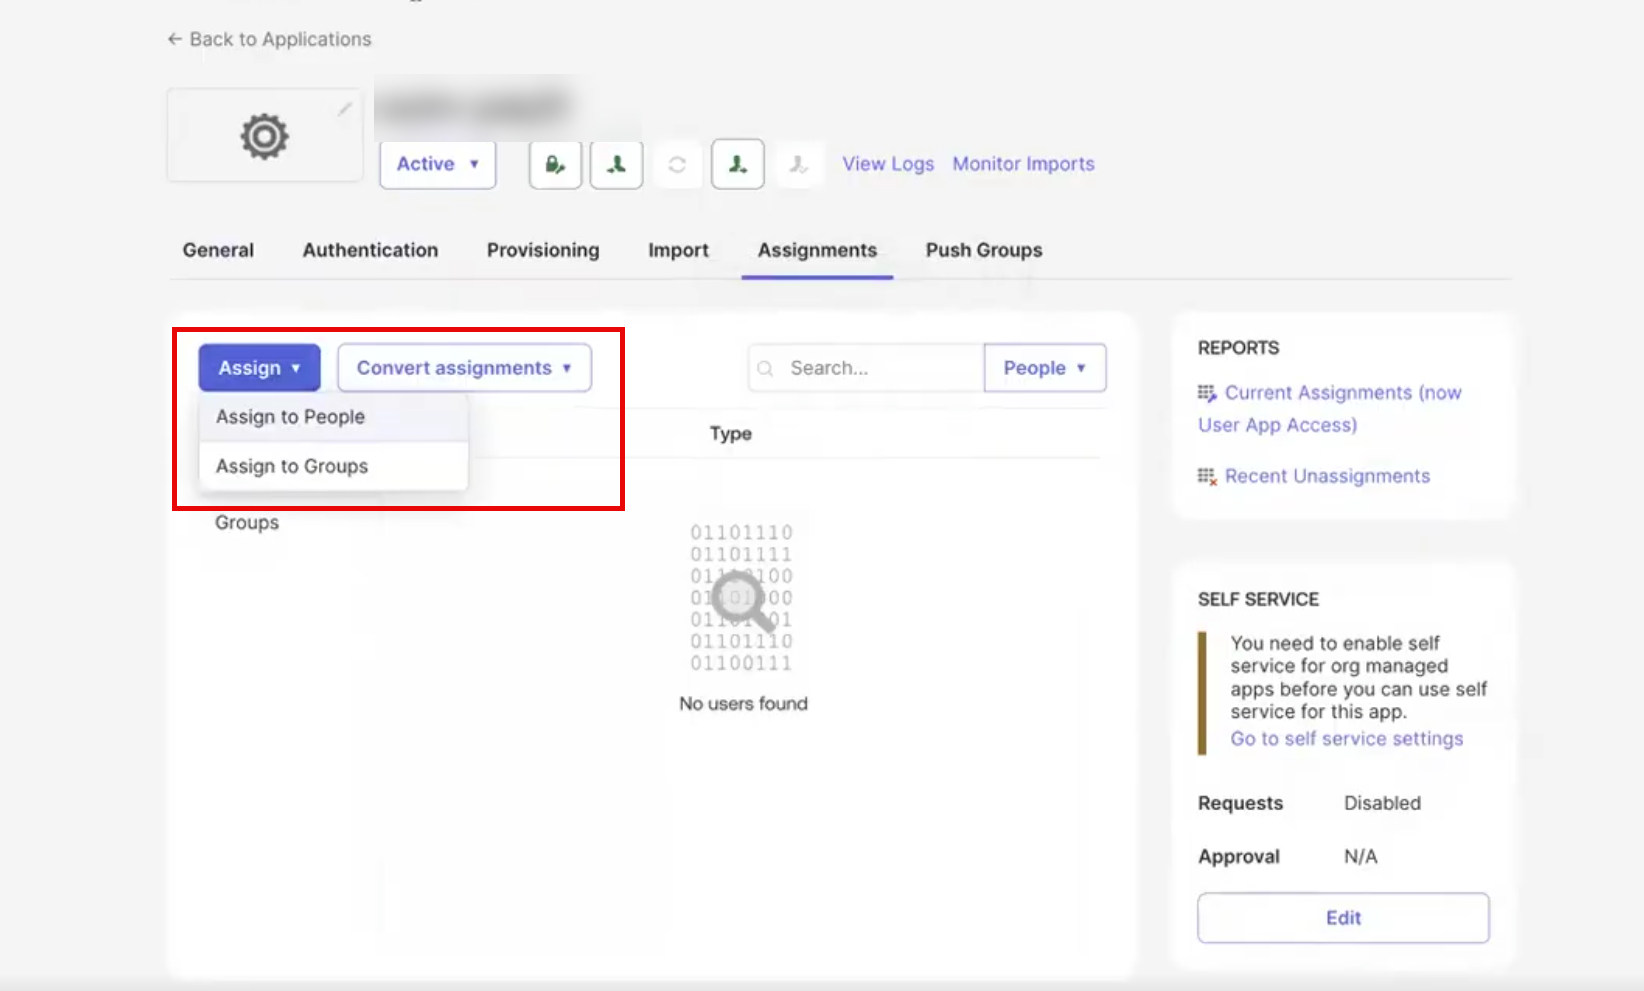
In the application Assignments tab, click
AssignAssign to Groups. Search for and select the group you created, then
click Save and Go Back >
Done.
Push the group to Strata Cloud Manager.
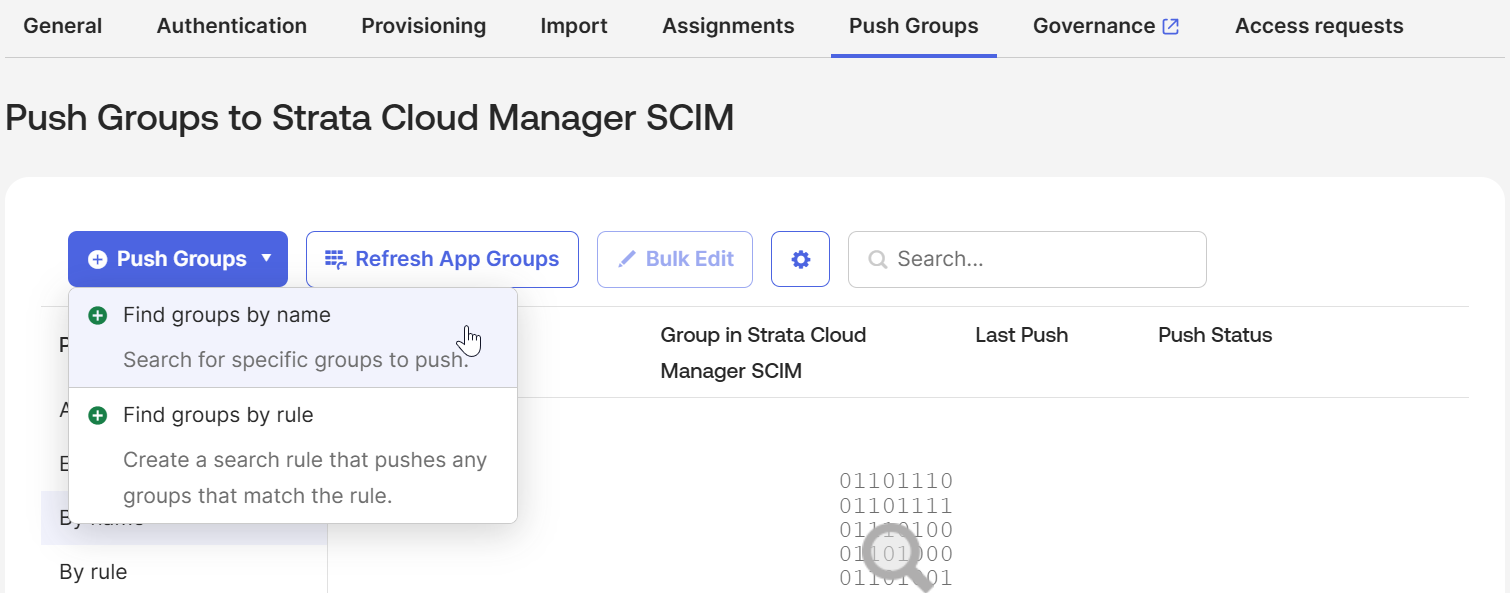
Select the Push Groups tab and click
Push GroupsFind groups by name. Search for the Okta group you created. Click the
drop-down arrow next to Create Group and
select Link Group. From the list of imported
Strata Cloud Manager roles, choose the target role you want to
map this Okta group to. Click
Save.
Always select Link Group
instead of Create Group during push group
configuration. Selecting Create Group causes
recurring synchronization errors because Strata Cloud Manager does
not support group creation through SCIM — only linking to existing
predefined roles.
Verify that the push group status shows Active.
An Active status confirms that Okta successfully linked the
group and is synchronizing membership with Strata Cloud Manager.
Verify user and group provisioning.
Confirm that users and groups provisioned through Okta appear correctly in Strata Cloud Manager with the expected role assignments.
Search for the users provisioned from Okta and verify that they appear
with the correct role assignments.
Identity and access changes may take a few minutes to propagate.
If provisioned users don't appear immediately, wait and refresh the
page.
Add users to a provisioned group.
Add new users to an Okta group that is already linked and pushed to Strata Cloud Manager. Users added to a linked group are automatically
provisioned to the corresponding Strata Cloud Manager role without any
additional push action.
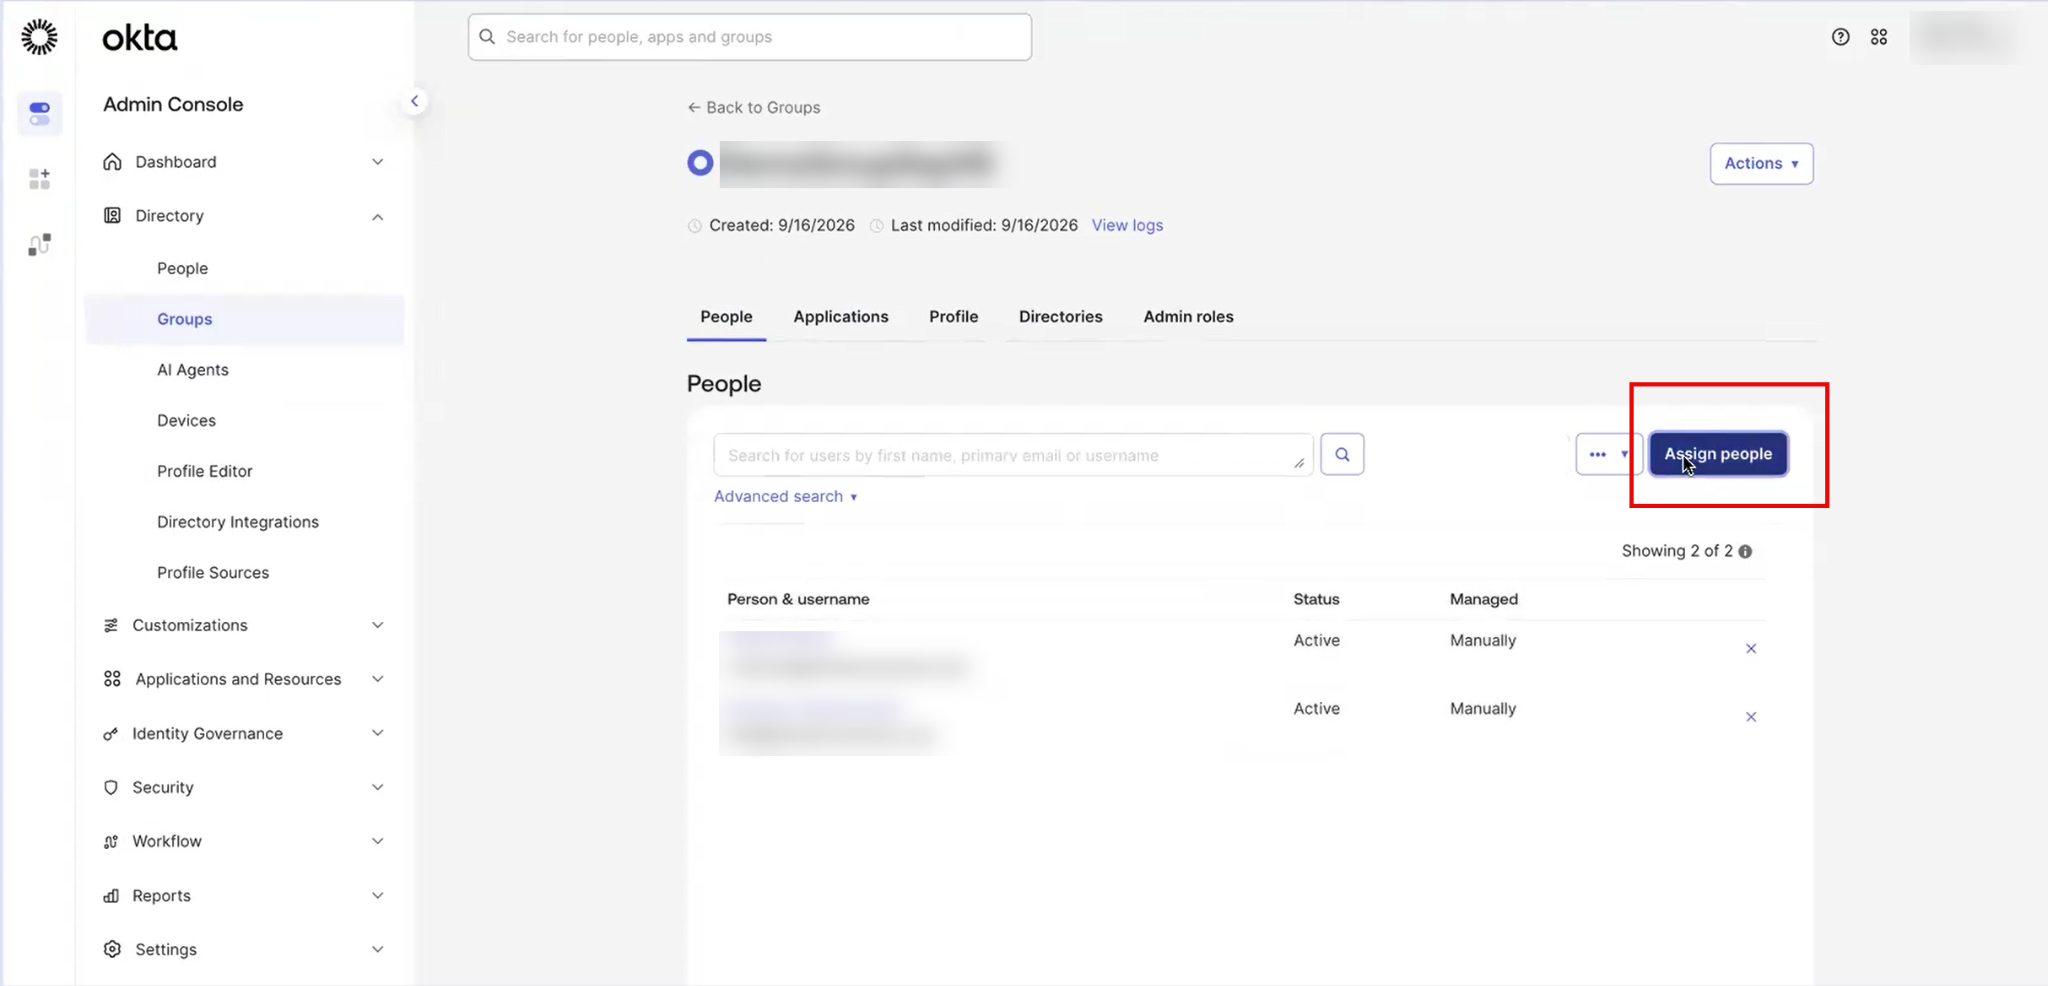
In the Okta Admin Console, navigate to DirectoryGroups.
Select the group that is linked to the Strata Cloud Manager
role.
Click Assign People.
Search for and select the users you want to add, then click
Done.
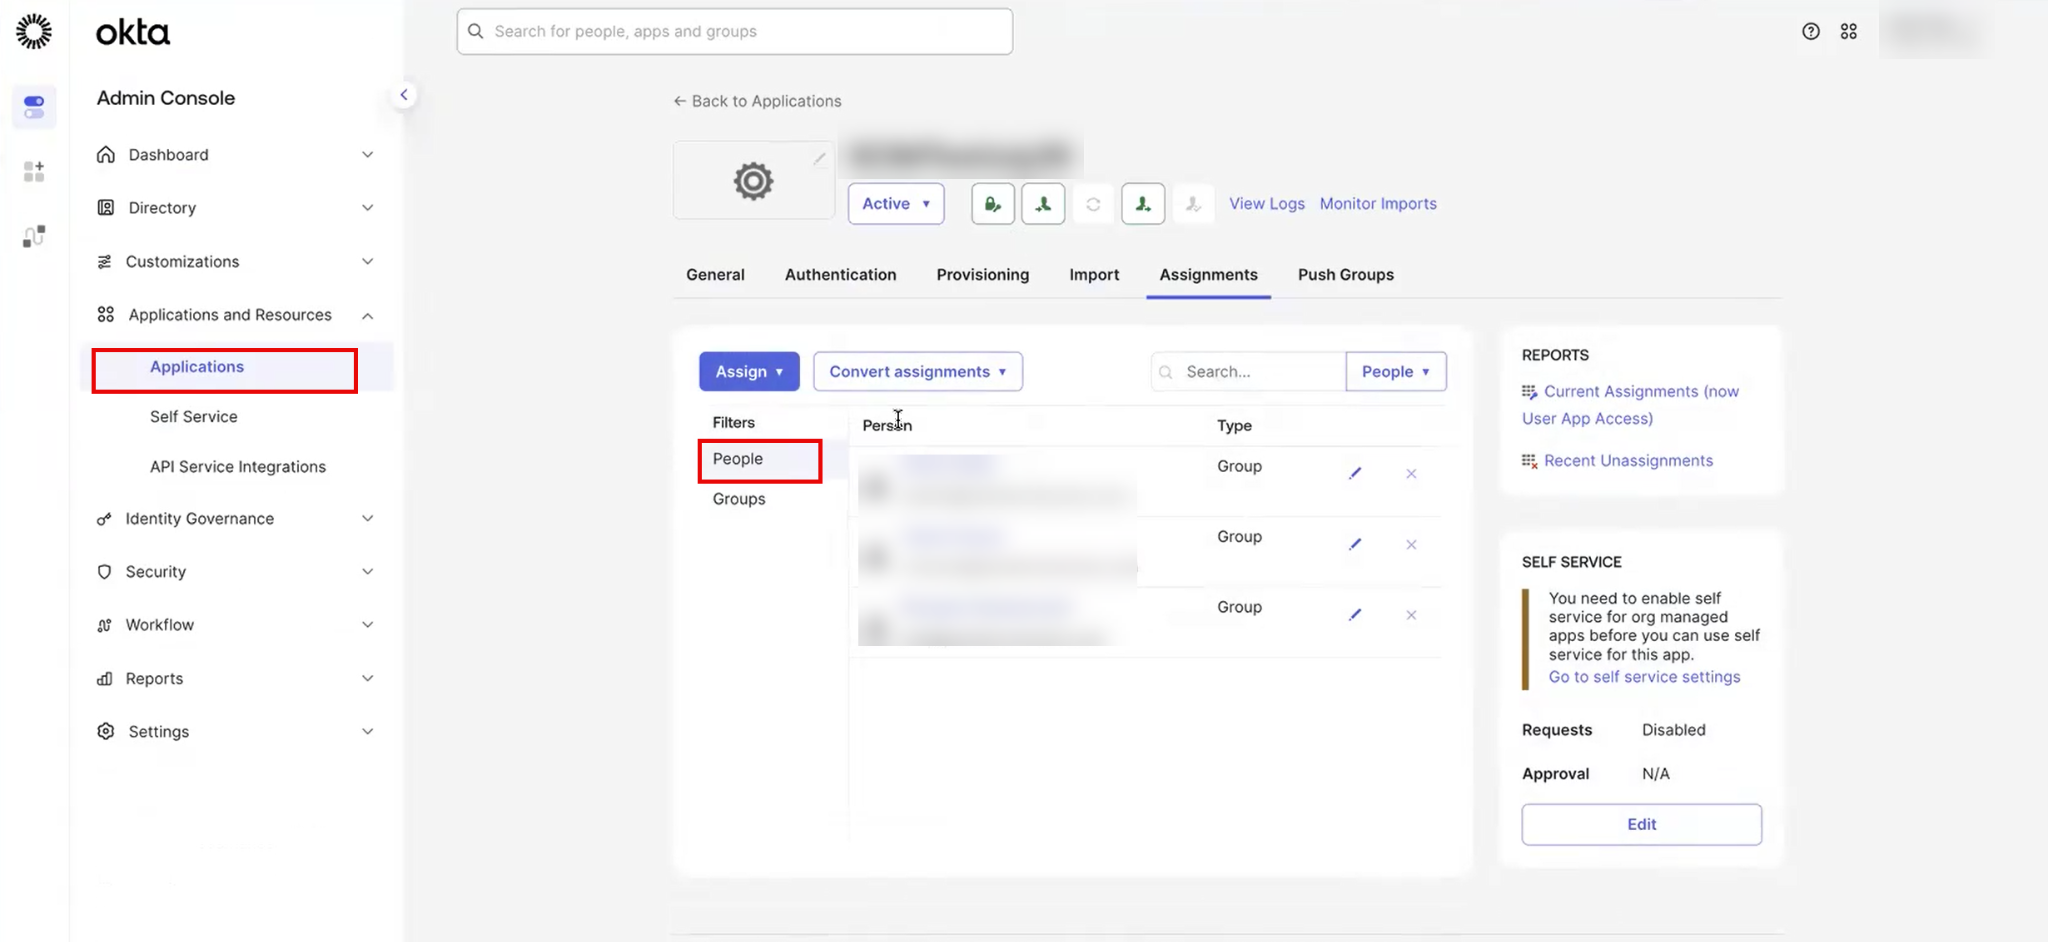
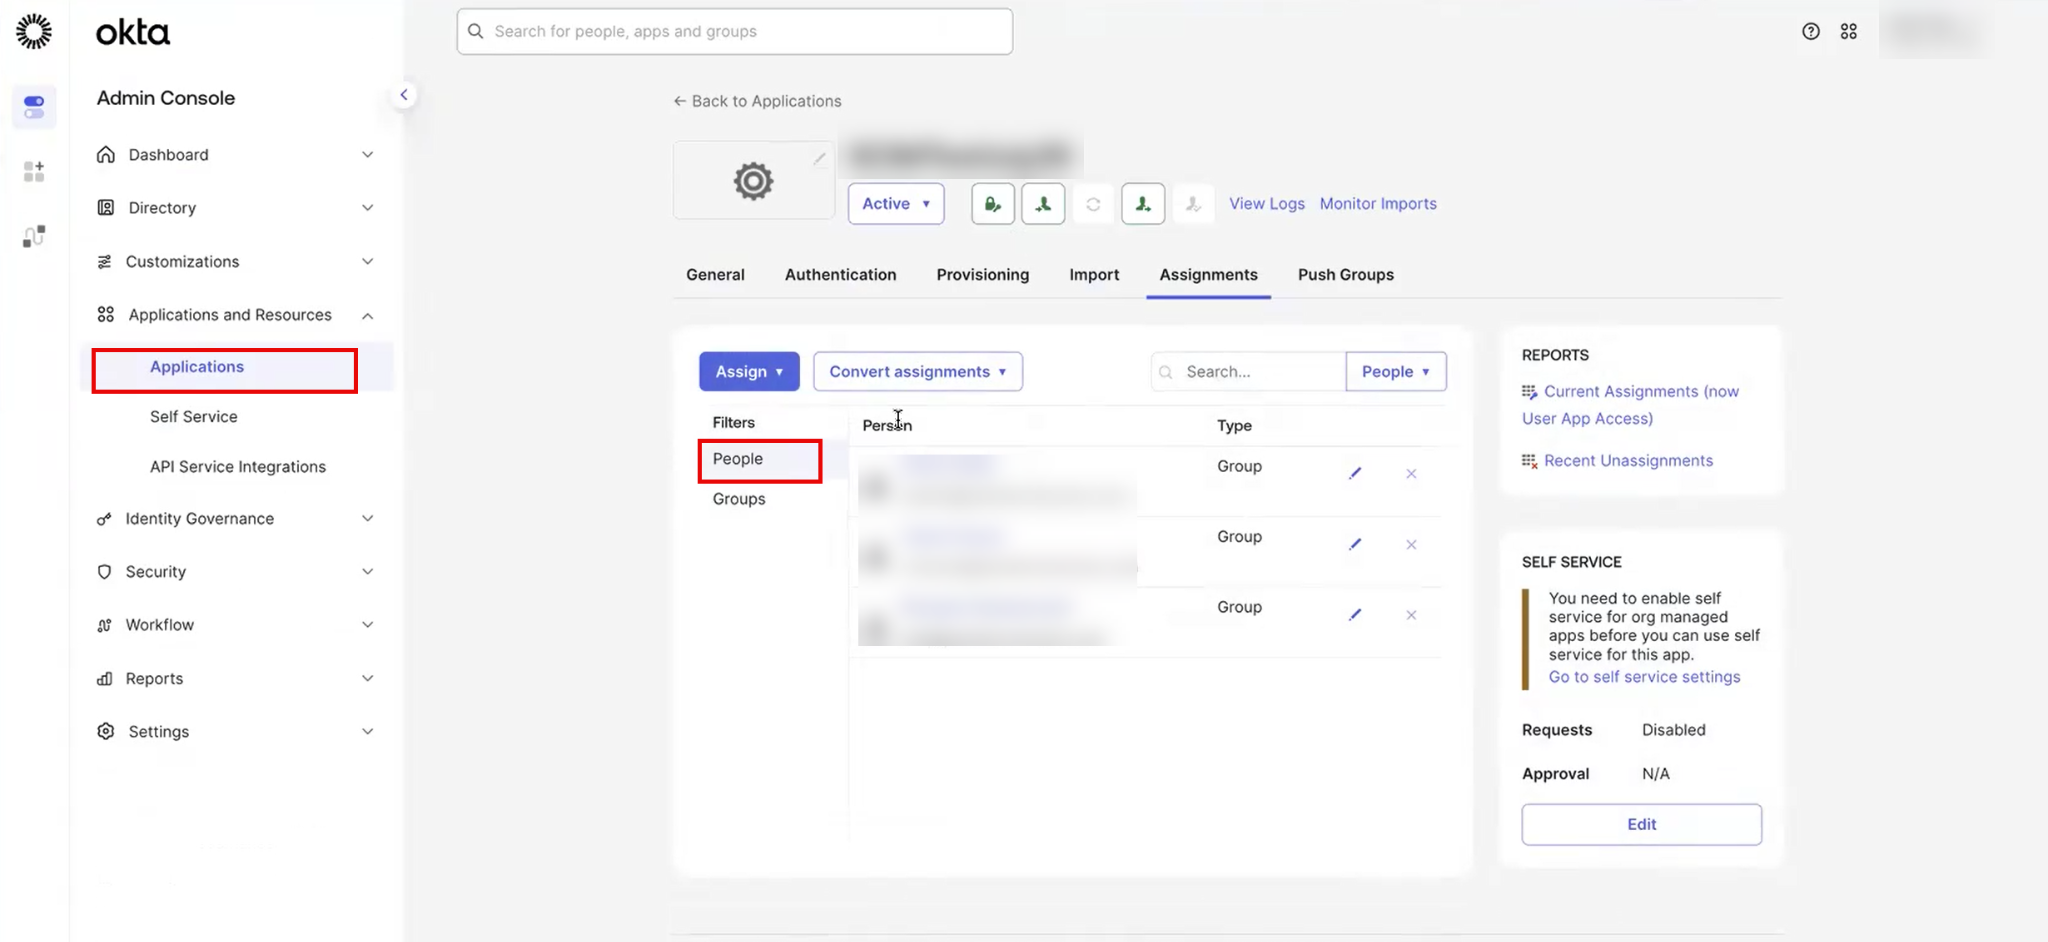
Navigate to Applications, select your Strata Cloud Manager SCIM application, then
select the People tab and verify that the newly
added users appear.
Log in to Strata Cloud Manager and navigate to SettingsIdentity & AccessAccess Management.
Verify that the newly added users appear with the expected role
assignment.
Adding users to a linked group automatically synchronizes them to
Strata Cloud Manager. You don't need to perform a manual
push.
Remove users from a provisioned group.
Remove users from an Okta group that is linked to a Strata Cloud Manager
role. Unlike adding users, removing users requires a manual push to
synchronize the change to Strata Cloud Manager.
In the Okta Admin Console, navigate to DirectoryGroups.
Select the group that is linked to the Strata Cloud Manager
role.
Click the X next to the user you want to remove from the
group.
Navigate to Applications, select your Strata Cloud Manager SCIM application, then
select the People tab and verify that the user
no longer appears.
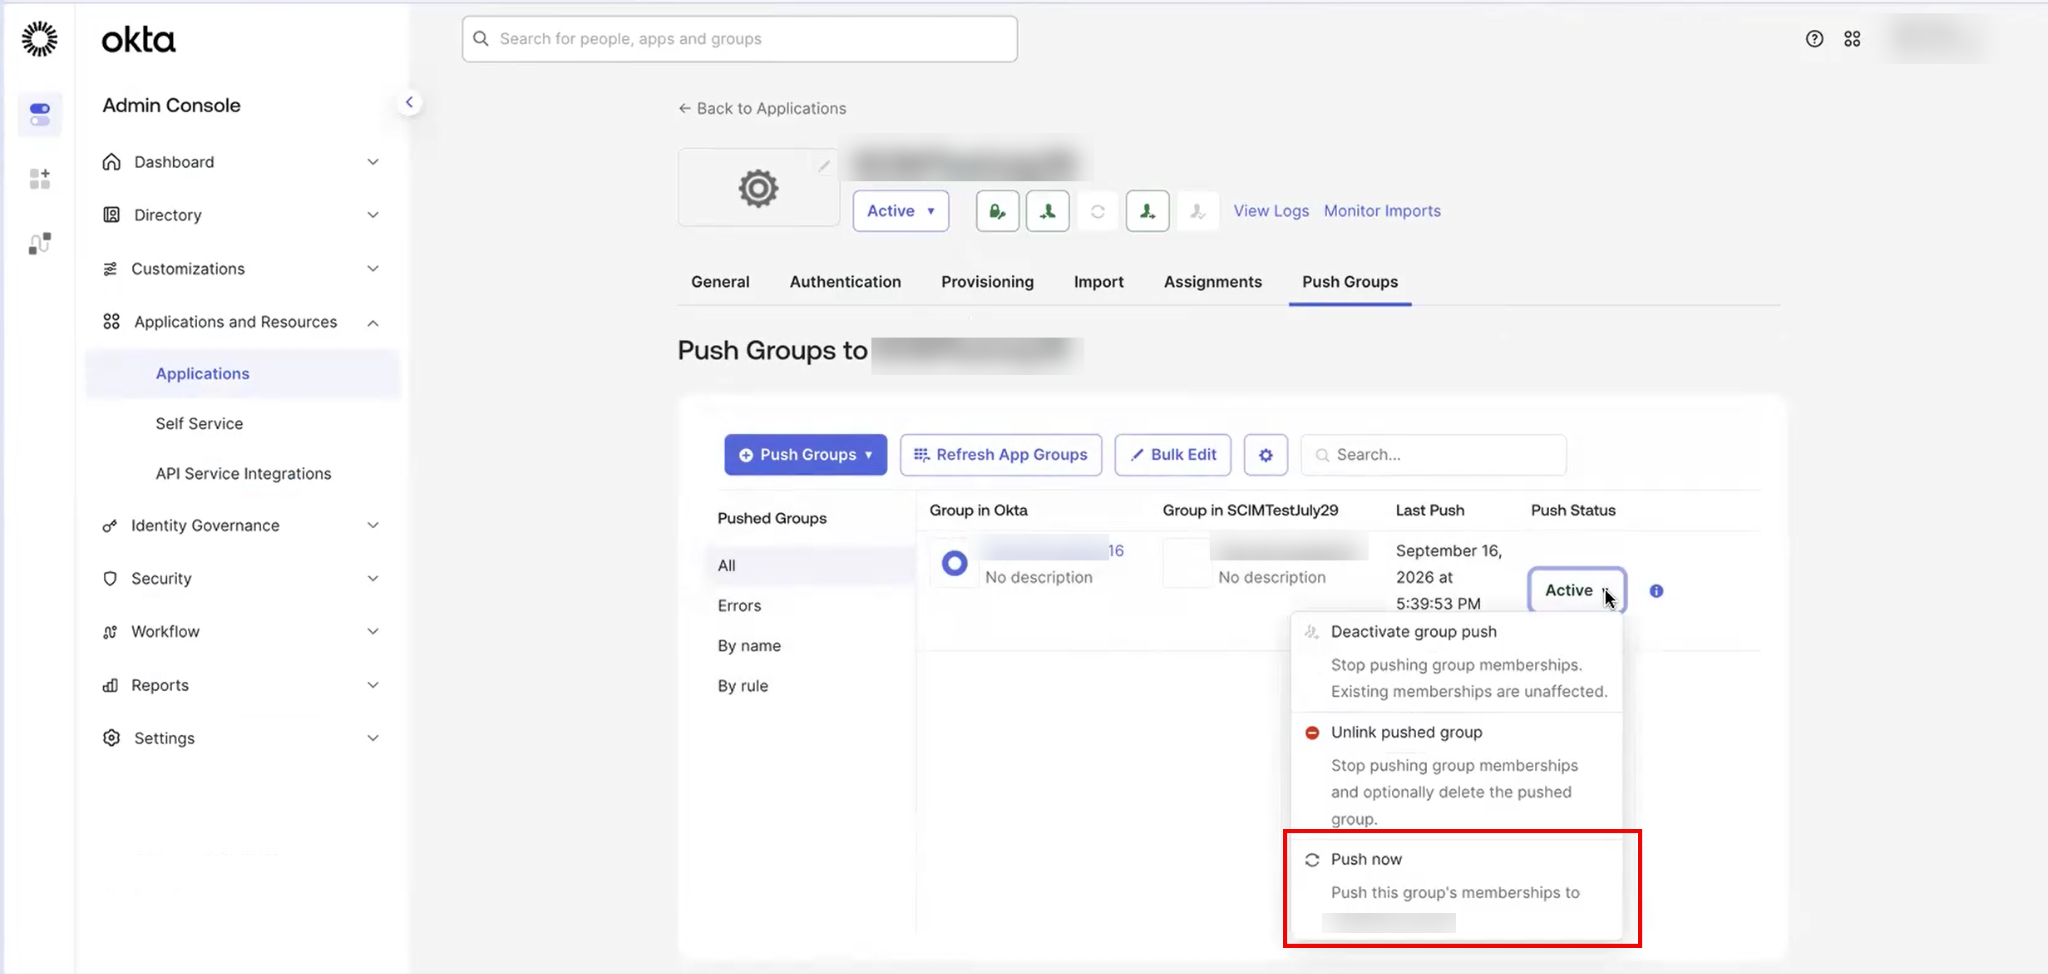
Select the Push Groups tab.
Click the arrow next to the Active status for the linked group
and select Push Now.
Wait for the push group status to return to Active.
Log in to Strata Cloud Manager and navigate to SettingsIdentity & AccessAccess Management.
Verify that the removed user no longer appears in the Strata Cloud Manager tenant.
Removing a user from the Okta group does not automatically remove
them from Strata Cloud Manager. You must manually push the group to
synchronize the removal. If you skip the Push
Now step, the user retains access in Strata Cloud Manager.
Remove and unlink a group from Strata Cloud Manager.
Remove a group assignment from the Okta application and unlink it from the
Strata Cloud Manager role. This process removes all users in the group
from the Strata Cloud Manager tenant and disconnects the group
mapping.
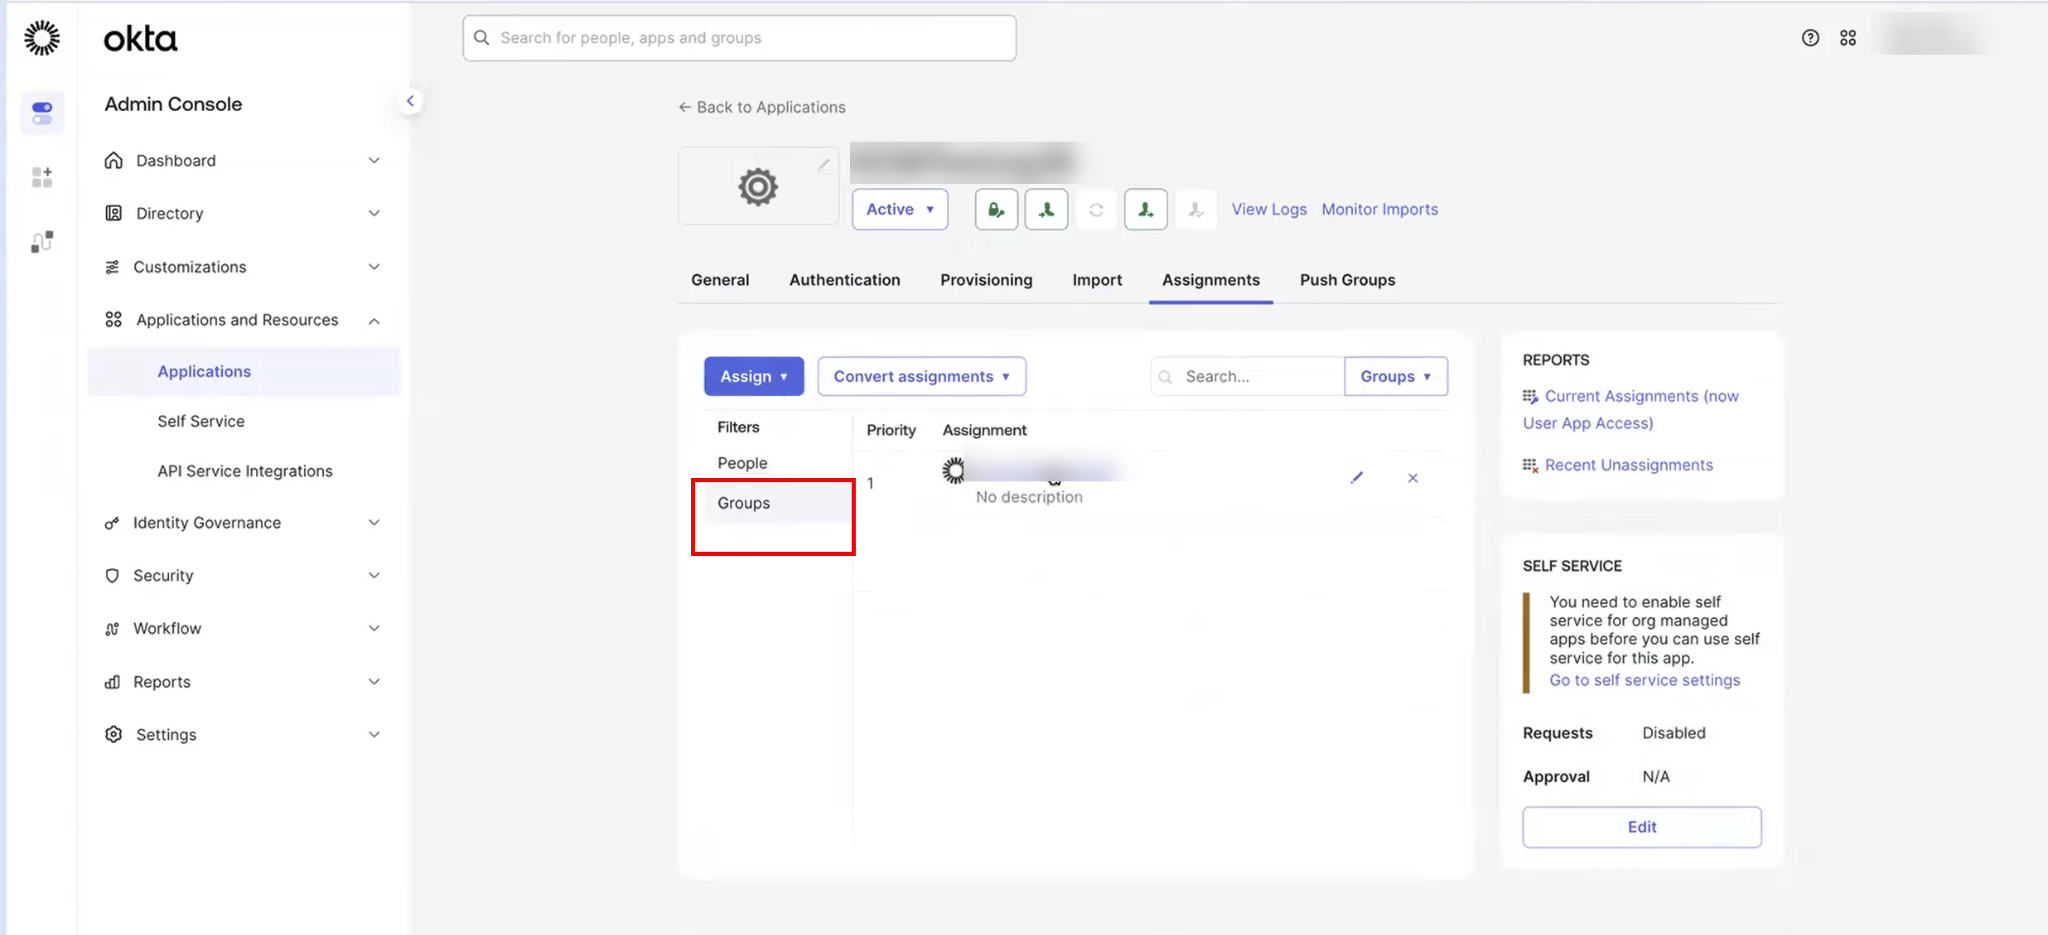
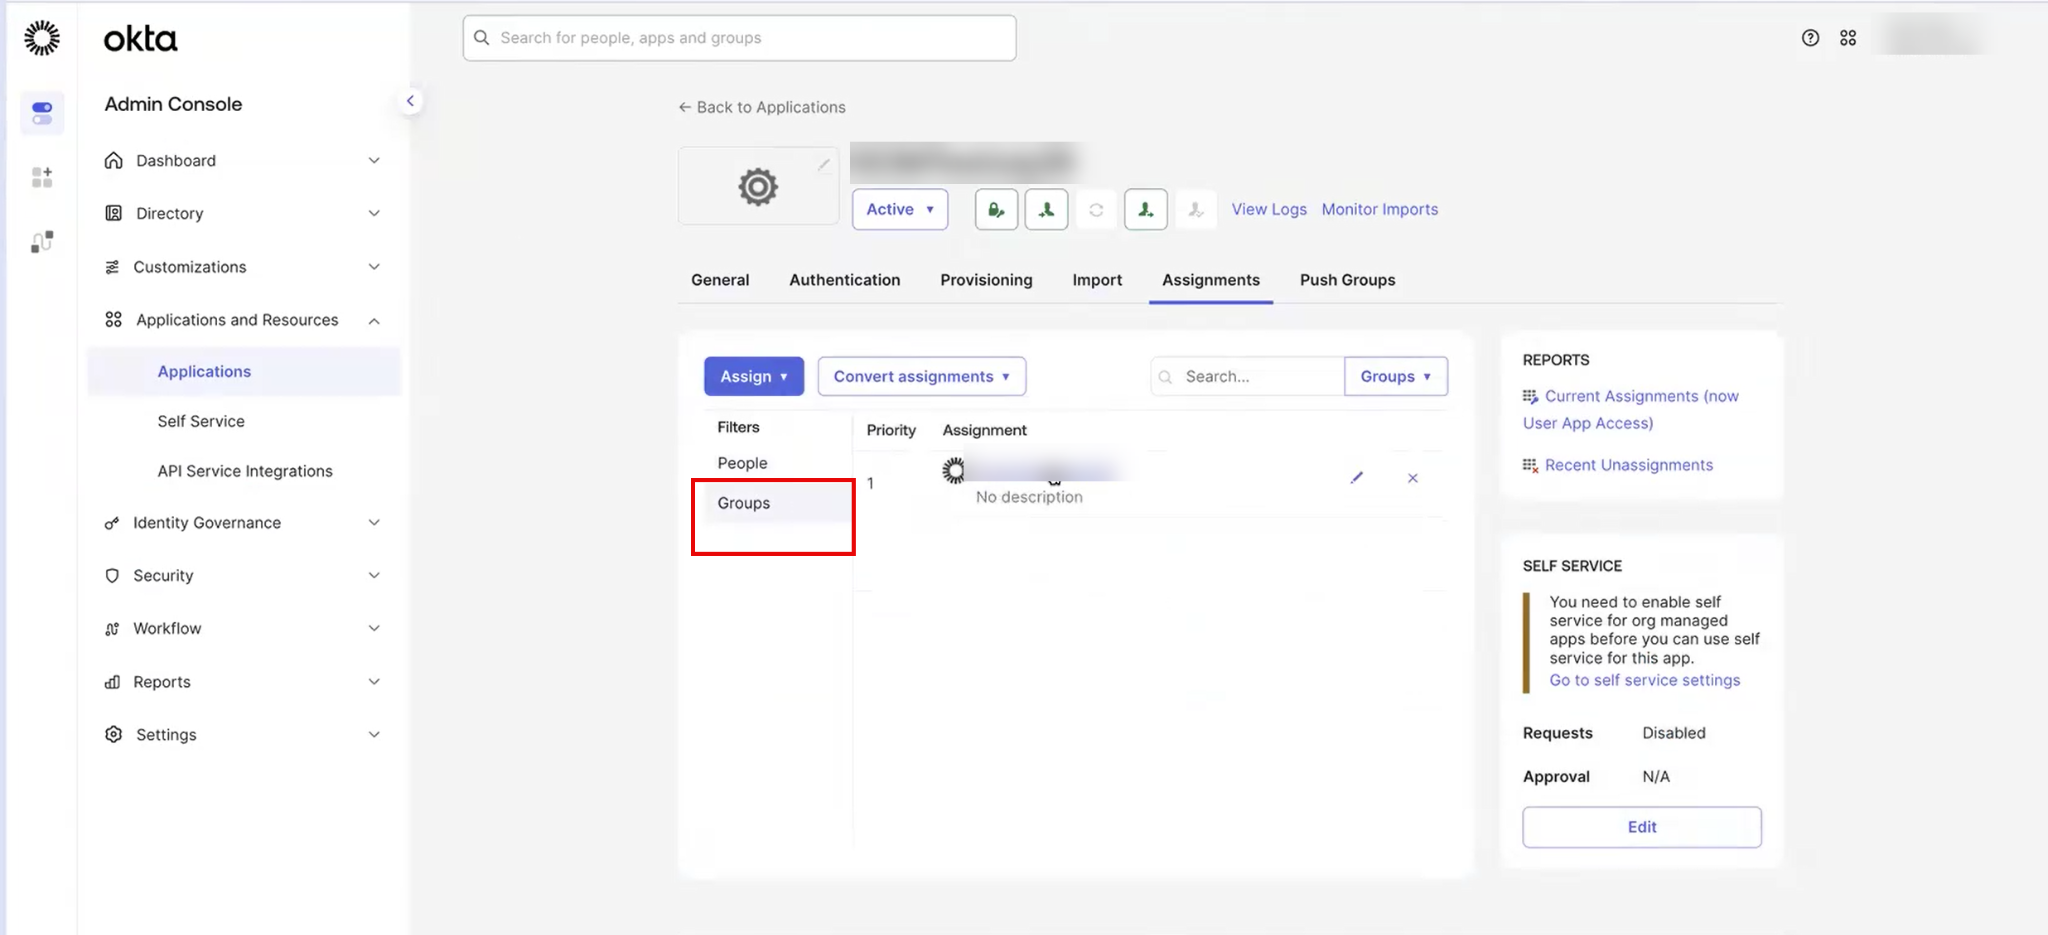
In the Okta Admin Console, navigate to Applications and select your Strata Cloud Manager SCIM
application.
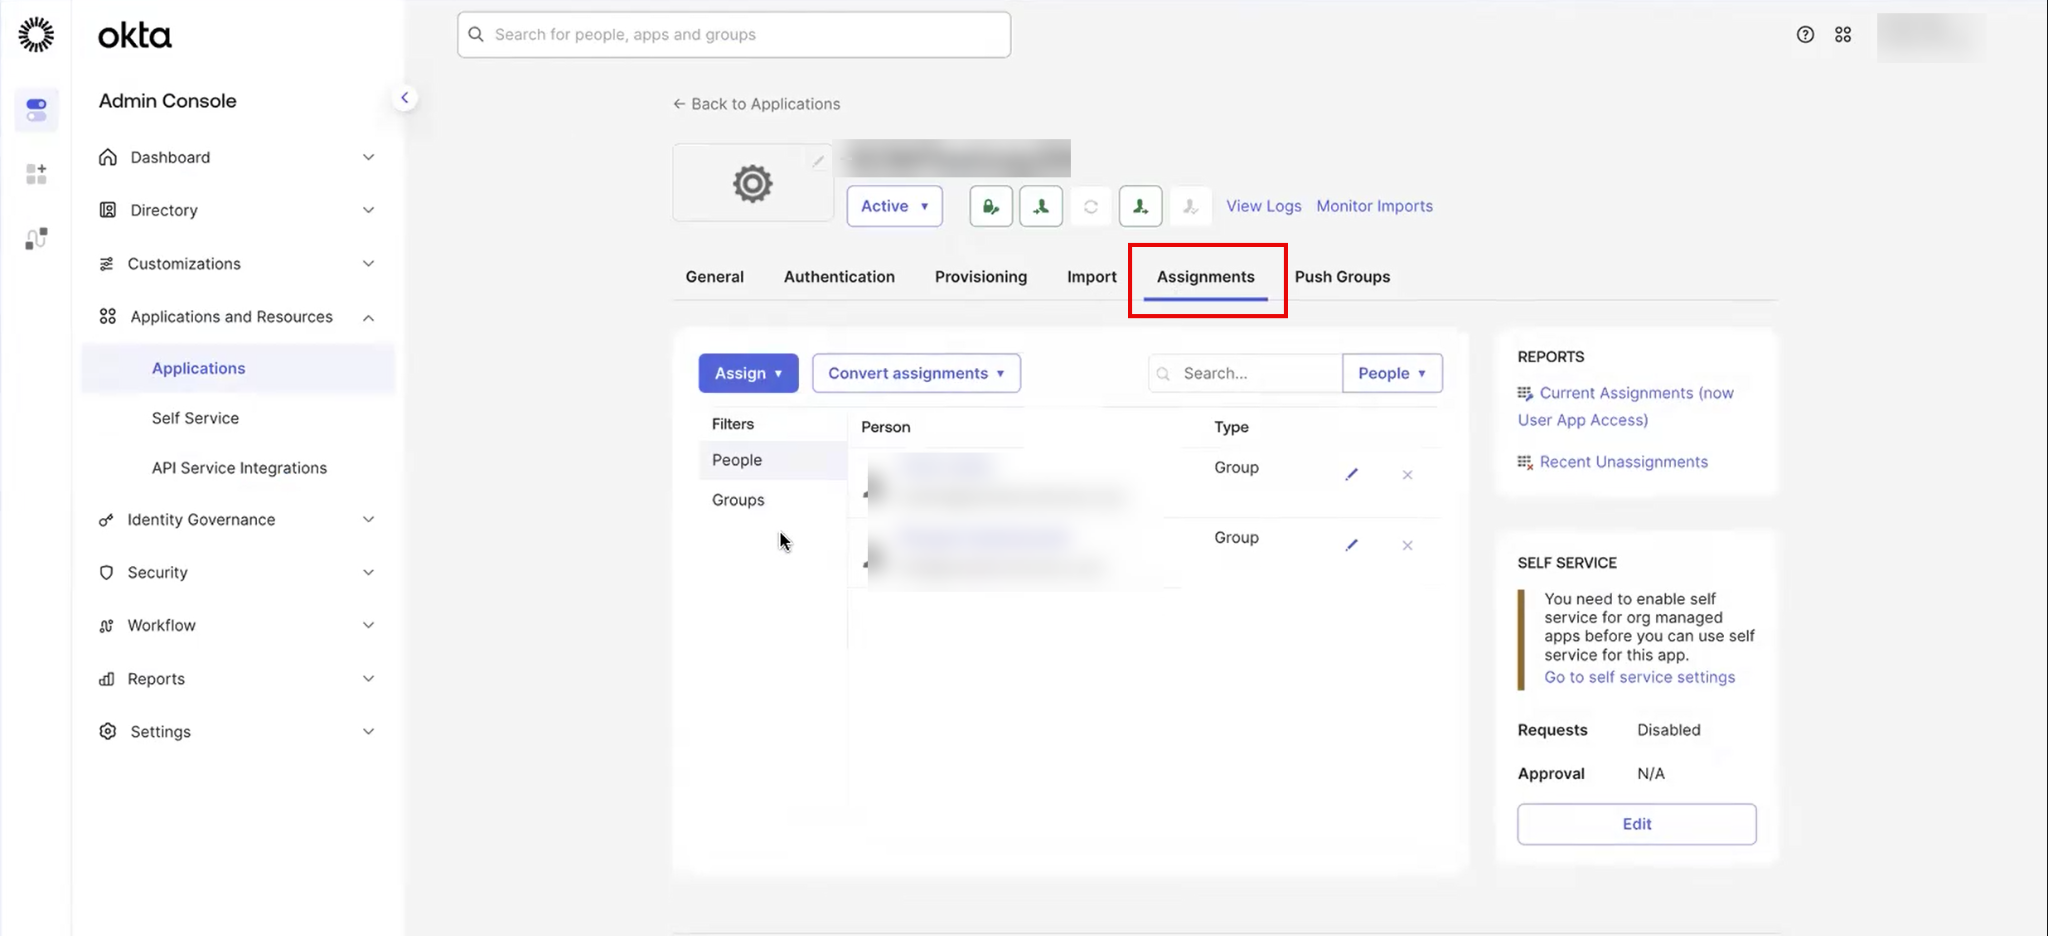
Select the Assignments tab.
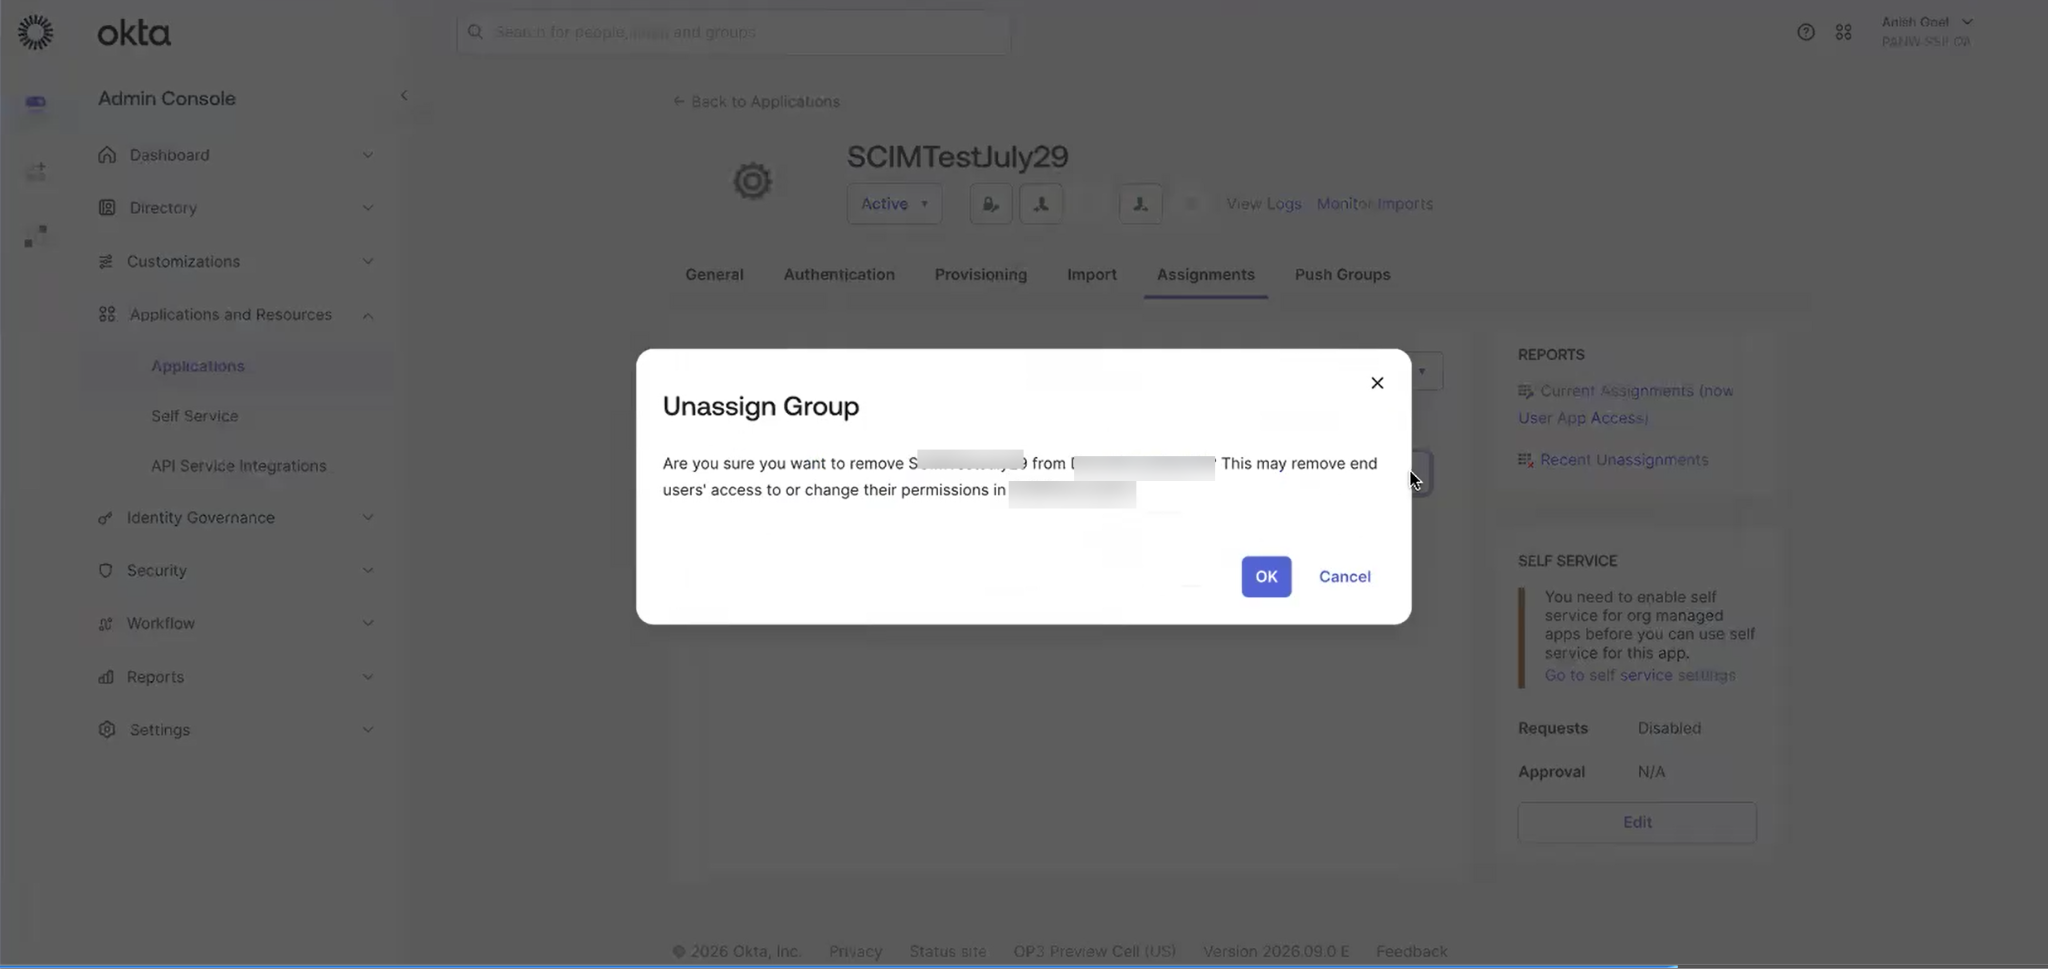
Locate the group under Groups and click
Remove to unassign the group from the
application.
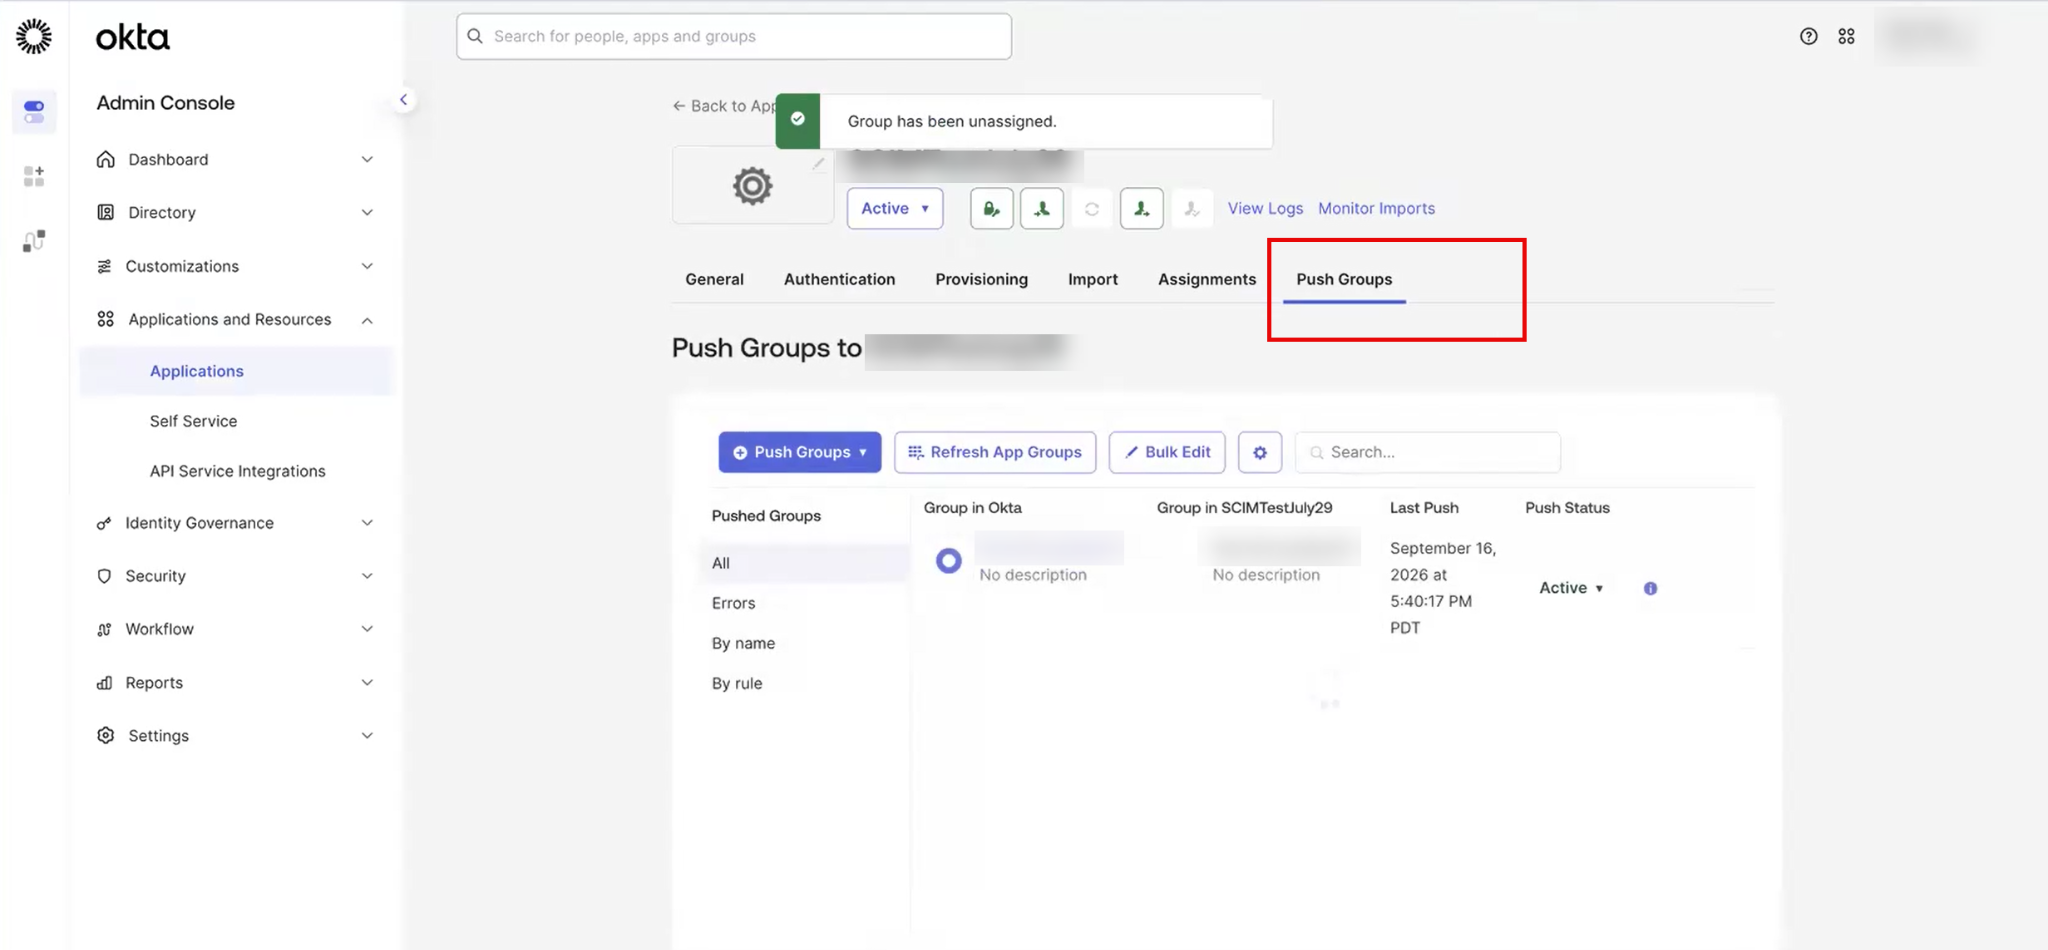
Select the Push Groups tab.
Click the arrow next to the Active status for the group and
select Push Now.
Wait for the push to complete and the status to return to
Active.
Log in to Strata Cloud Manager, navigate to SettingsIdentity & AccessAccess Management, and verify that the users from the removed group no
longer appear.
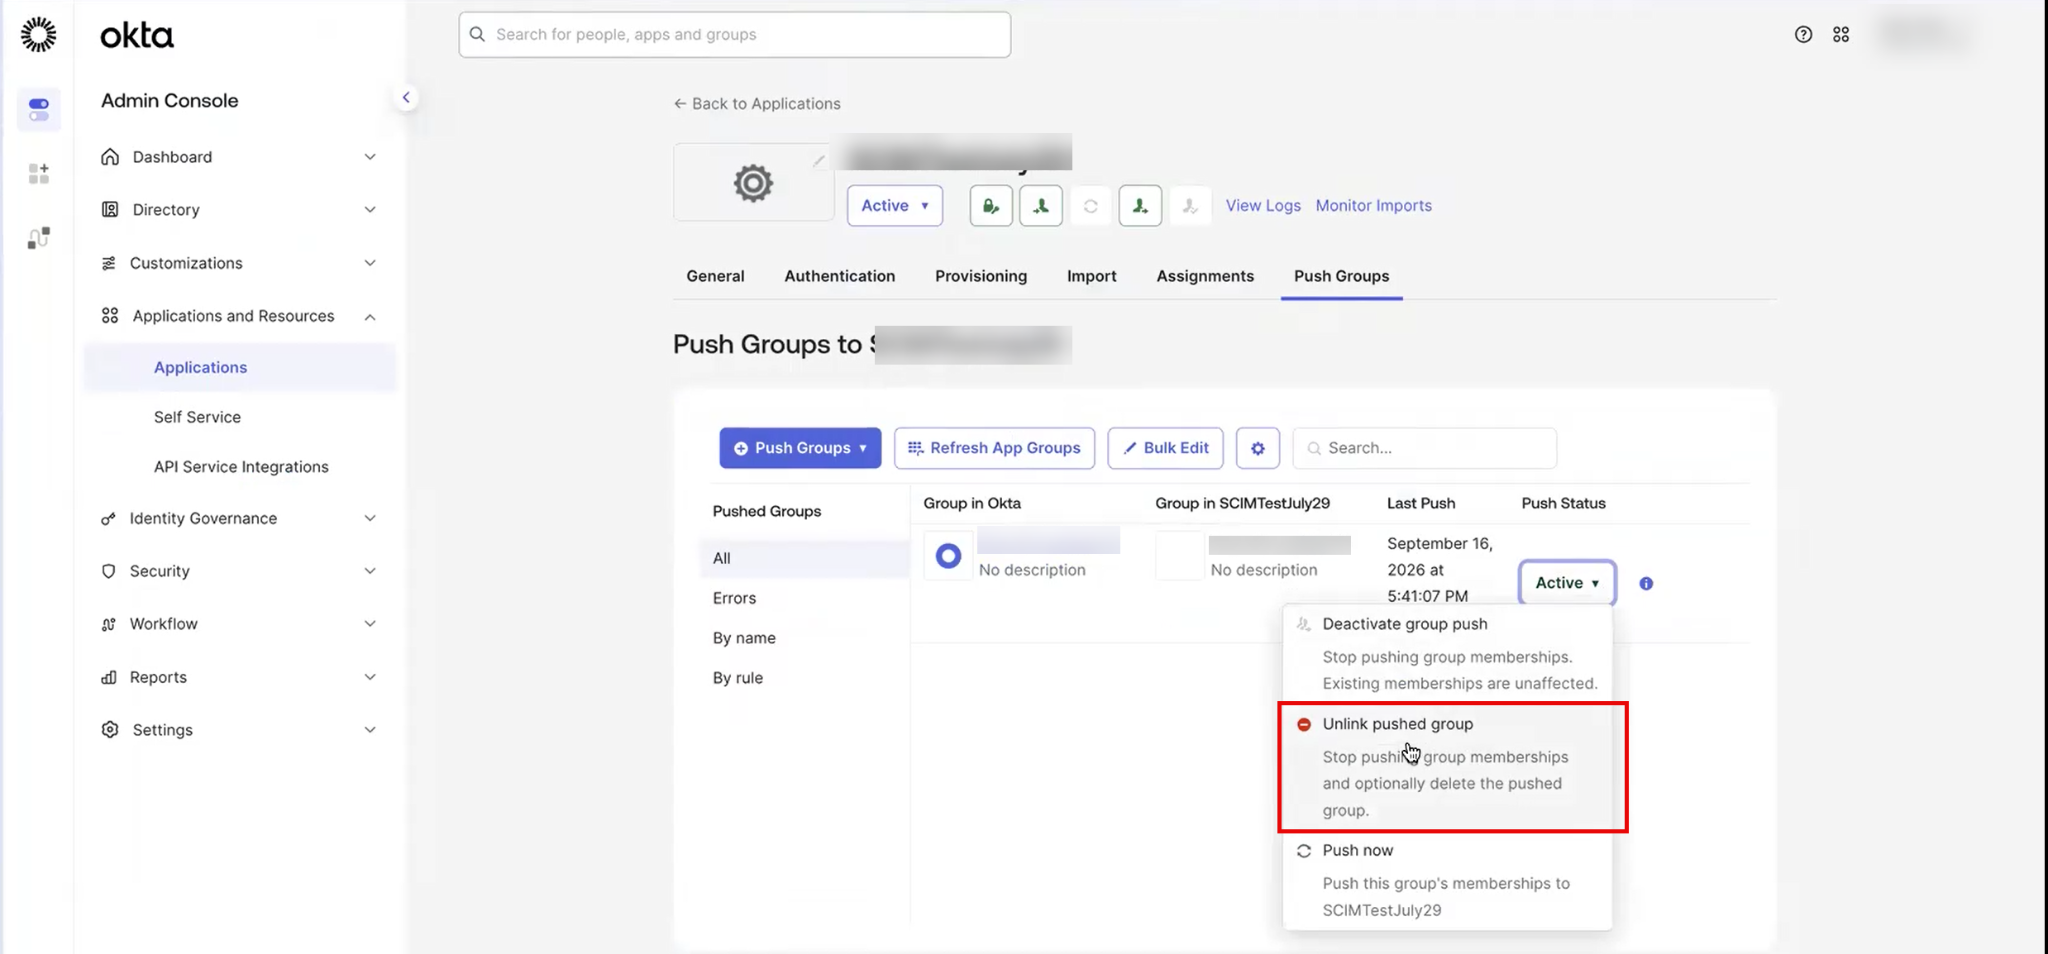
Return to the Okta application Push Groups
tab.
Click the arrow next to the group status and select Unlink
pushed group.
When prompted, select Leave the group in the target
app and click
Unlink.
Unassigning the group from the application alone does not remove
users from Strata Cloud Manager. You must push the change and then
unlink the group to fully disconnect the mapping. The Leave
the group in the target app option preserves the Strata Cloud Manager role definition while removing the Okta
synchronization link.